Forgot your password?
typodupeerror

Comment Re:That's not hard (Score 1) 48

The XuanTie C910 RISC V CPU exists. They probably chose the ARM baseline for its compatibility with Harmony which includes automated binary translation layers (similar to Apple's Rosetta 2) and can run x86 Windows binaries on Kirin processors out of the box. So the buyers can keep running all of their older pirated MS office apps.

Comment Happened 15 years ago (Score 1) 89

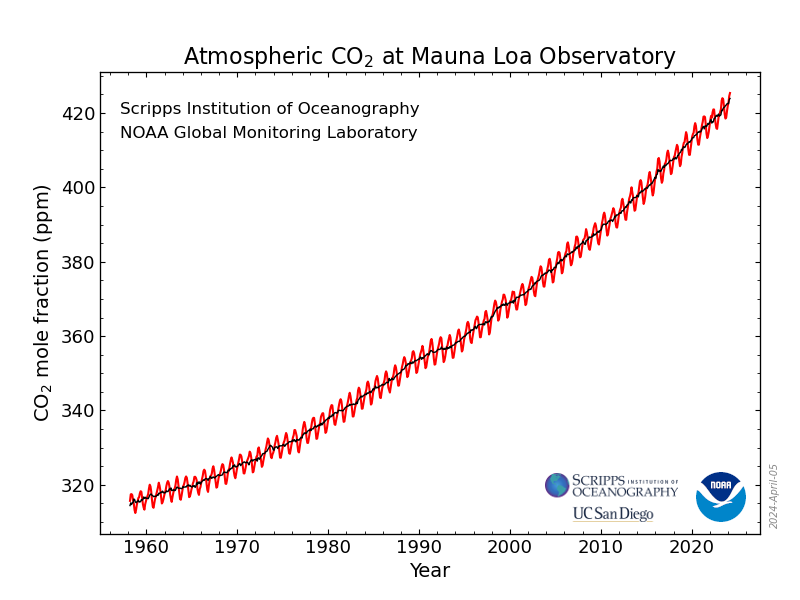
Climatology numbers are all based on 30 year averaging. Global warming trends are all monotonic and slightly better than linear. So, climatology predictions about tomorrow happened 15 years ago. 6% of the world's glaciers are already permanently gone, 19% of Central Europe's glaciers are permanently gone. This "future" damage is well in progress because the numbers "predicted" have already happened.

Comment More Human Harvesting ... nothing to see here (Score 1) 129

Companies do this for one reason: They can monetize their customers via the app. A value extraction consultant has made a successful pitch to the executives at Mitsubishi UFJ Financial Group and now the sales job on why this is better for customer is in full swing. For "security reasons", the app will require precision geolocation.

Comment No need for pesky warrants (Score 1) 63

Decisions like this are why so many law enforcement agencies simply buy access to location databases from companies like Gravy Analytics, Fog Data Services and Venntel. This data is much better than a geofence of a single tower for a narrow time window. You can follow the people to their homes, figure out groups of people who traveled together, correlate their travels with a specific car, etc.

Somehow writing a check to trample the constitution is a completely different thing than directly trampling the constitution.

Comment Re:So embedded TV apps are getting routable IPs? (Score 1) 31

The TVs do not need routable IP addresses; they just need to behind a router that supports The UPnP Internet Gateway Device (IGD) profile -- and most home routers support this protocol. Then it is a simple SOAP request to the router by the app to get a port mapped.

Comment Re:Don't ever use hotel WiFi (Score 2) 31

In some cities like D.C., New York, Paris the time between the time you join the hotel network and are attacked is less than 5 minutes. It is fun to travel with WireShark and watch this, but not with a computer you care about. So yes, use your cell phone, not the hotel network.

It is more common than people realize that these BusyBox based cheap commodity network servers suffer a regression where test code is accidentally included in a given release. When that happens, the devices are quickly owned. That may not be the case here, but have seen this exact issue in a worldwide hotel chain almost 5 years ago.

Comment Another example of failed U.S. governance (Score 3, Insightful) 47

These attacks prove that leaving individual cities to fend for themselves on the open commercial internet is a complete failure of public governance. The fact that small towns in these states are actively fighting off what U.S. officials believe are foreign, state-sponsored adversaries like Iranian hackers highlights the sheer absurdity of our decentralized approach. Cybersecurity inherently scales; while Fortune 100 companies protect thousands of endpoints for pennies per user using enterprise-grade automation, resource-starved municipalities are forced to survive with tiny budgets and skeleton IT crews.

South Dakota is the only state that endeavors to give a protected network to its municipalities. Five years after Oldsmar Florida exposed this exact vulnerability, we are watching the exact same script play out as utility operators across the country are forced to switch to manual workarounds to keep their treatment plants online. For a fraction of the millions spent reacting to these disruptions, states could easily pool their buying power to build a single, hardened network infrastructure for every municipal utility. The refusal of almost all of our states or the federal government to implement a sane, centralized defense model like South Dakota's means American critical infrastructure remains an open, fragmented playground for cybercriminals.

And an "I told you so": I stated in the first post on this when Minnesota was the only state named that the rest of the states were simply incapable of noticing. Now we have 7 states -- the attacks are likely against all.

Comment Claim 23 is incorrect (Score 1) 132

The attorneys for Op-Fortitude do not seem to know the difference between encryption keys and encrypted content.

"If the DCP is encrypted, please have the keys open from the time the asset lands through EOD on 6/16. This timing allows us to test the content and ensure a streamlined screening." In other words, Netflix expressly requested that the Film's DCP be either unencrypted or unlocked.

A request that keys be valid for a given time period is very different from a request that content be a-priori unlocked. Everything following "In other words" is a false assertion and this assertion is then a lynchpin for following claims. So claim 23 being false unravels much of the pleading.

The fact that there is no mention of the movie industry standard Digital Cinema Initiatives (DCI) in the pleading while referring to the event as a "screening" is a giant red flag. Keys are always time bounded in DCI and Netflix was likely assuming that they would be receiving DCI protected content when they made this request in this way. Either these attorneys are not too bright or more likely they are working with a client that requires a certain amount of willful ignorance on their part (In which case they already are expecting to lose this but are going to bill as many hours as possible in the process).

Comment The lack of previous resolution left IBM exposed (Score 2) 109

Despite the fact that SCO's attorneys were on the verge of being sanctioned for failing to produce any evidence last time, the way the case ended is SCO and IBM both just dropped the case without real resolution. Now we have a savvy attorney from Xinuos making the argument:

"But if we thought that infringement claims accrue at the time of copying, it might be that if IBM then uses the code again at a later time, there's a new infringement claim."

Even though exactly what was initially copied by IBM that was uniquely SCO content was never really made clear by SCO despite years of legal maneuvering.

This is just old fashioned gray mail. The only reason Xinuos exists is to extort money from IBM, so that is what they are going to do.

Slashdot Top Deals

Genetics explains why you look like your father, and if you don't, why you should.

Working...