Printer

Ask Slashdot: Will We Ever Be Able To Make Our Own Computer Hardware At Home? 117

dryriver writes: The sheer extent of the data privacy catastrophe happening -- everything software/hardware potentially spies on us, and we don't get to see what is in the source code or circuit diagrams -- got me thinking about an intriguing possibility. Will it ever be possible to design and manufacture your own CPU, GPU, ASIC or RAM chip right in your own home? 3D printers already allow 3D objects to be printed at home that would previously have required an injection molding machine. Inkjet printers can do high DPI color printouts at home that would previously have required a printing press. Could this ever happen for making computer hardware? A compact home machine that can print out DIY electronic circuits right in your home or garage? Could this machine look a bit like a large inkjet printer, where you load the electronics equivalent of "premium glossy photo paper" into the printer, and out comes a printed, etched, or otherwise created integrated circuit that just needs some electricity to start working? If such a machine or "electronics printer" is technically feasible, would the powers that be ever allow us to own one?
Advertising

If Logged Into Facebook, Oculus VR Data Will Now Be Used For Ads (uploadvr.com) 36

"Facebook will now use information about your Oculus activity, like which apps you use, to help provide [...] more relevant content, including ads" -- assuming you've connected your Oculus ID to your Facebook account. UploadVR reports: The company is updating its privacy policy and rolling out new social VR features backed by your "Facebook identity" with the intention of "clarifying how Oculus data is shared with Facebook to inform ads when you log into Facebook on Oculus." "These changes won't affect third-party apps and games, and they won't affect your on-device data," according to the company. For years now, buyers of Facebook VR headsets needed an Oculus ID to operate the system that could be optionally connected to your "Facebook identity" -- in other words, you could connect the two accounts. More recently, to access certain features like concerts in Venues, Facebook started requiring the use of the Facebook account. According to the company's terms, this account "must ... use the same name that you use in everyday life."

With this most recent change "If you choose not to log into Facebook on Oculus, we won't share data with Facebook to allow third parties to target advertisements to you based on your use of the Oculus Platform," according to Facebook. But denying that connection may also make it difficult to connect with others using virtual reality on Oculus systems. [...] Facebook suggests that for those who log into the account it will target "relevant content" based around "Oculus activity" including "which apps you use" with examples given including "Oculus Events you might like to attend or ads for VR apps available on the Oculus Store." The company says this "won't affect your on-device data" which, based on our previous reporting, Facebook says is the location where "3D maps of your environment" are kept. "We don't collect and store images or 3D maps of your environment on our servers today -- images are not stored anywhere, and 3D maps are stored locally on the headset [for Quest] and on your local PC, where you have access to delete it [for Rift S]," a Facebook representative originally wrote in an email.
Facebook also says the changes "won't affect third-party apps and games" and "if you choose not to log into Facebook on Oculus, we won't share data with Facebook to allow third parties to target advertisements to you based on your use of the Oculus Platform."
Security

Maze Ransomware Was Behind Pensacola 'Cyber Event,' Florida Officials Say (arstechnica.com) 5

An anonymous reader quotes a report from Ars Technica: An email sent by the Florida Department of Law Enforcement to all Florida county commissioners indicated that the ransomware that struck the city of Pensacola on December 7 was the same malware used in an attack against the private security firm Allied Universal, according to a report by the Pensacola News Journal. That malware has been identified elsewhere as Maze, a form of ransomware that has also been distributed via spam email campaigns in Italy.

Bleeping Computer's Lawrence Abrams reported in November that the Maze operators had contacted him after the Allied Universal attack, claiming to have stolen files from the company before encrypting them on the victims' computers. After Allied apparently missed the deadline for payment of the ransom on the files, the ransomware operators published 700 megabytes of files from Allied and demanded 300 Bitcoins (approximately $2.3 million) to decrypt the network. The Maze operators told Abrams that they always steal victims' files to use as further leverage to get them to pay: "It is just a logic. If we disclose it who will believe us? It is not in our interest, it will be silly to disclose as we gain nothing from it. We also delete data because it is not really interesting. We are neither espionage group nor any other type of APT, the data is not interesting for us."
"The use of the data to blackmail the victim, and in Allied's case, the threat to use Allied's certificates and domain name to spam customers with additional ransomware attacks, is something new," writes Sean Gallagher.

"This is the first time this has ever happened, as far as we know," said Brett Callow, a spokesperson for the antivirus software vendor Emisoft. "Ransomware groups usually encrypt, not steal. We expect data exfiltration to become more and more commonplace. Whether Pensacola's data was exfiltrated, I obviously can't say."
Microsoft

Microsoft is About To Start Aggressively Advertising Windows 10 To Windows 7 Stragglers (betanews.com) 266

Mark Wycislik-Wilson, writing for BetaNews: Having already started to notify Windows 7 hangers on that support is due to come to an end, Microsoft is now ready to get a little more aggressive. If you haven't moved on from Windows 7, soon you will see full-screen notifications warning you that "your Windows 7 PC is out of support." The messages are due to be displayed from the day after support ends. So when January 15 rolls around, anyone who has doggedly stuck with Windows 7 will find that they not only have no support and no security updates, but also that they are pestered by an invasive message delivered by a program called EOSnotify.exe.
Encryption

Apple Used the DMCA to Take Down a Tweet Containing an iPhone Encryption Key (vice.com) 66

Security researchers are accusing Apple of abusing the Digital Millennium Copyright Act (DMCA) to take down a viral tweet and several Reddit posts that discuss techniques and tools to hack iPhones. Lorenzo Franceschi-Bicchierai, reporting for Vice: On Sunday, a security researcher who focuses on iOS and goes by the name Siguza posted a tweet containing what appears to be an encryption key that could be used to reverse engineer the Secure Enclave Processor, the part of the iPhone that handles data encryption and stores other sensitive data. Two days later, a law firm that has worked for Apple in the past sent a DMCA Takedown Notice to Twitter, asking for the tweet to be removed. The company complied, and the tweet became unavailable until today, when it reappeared. In a tweet, Siguza said that the DMCA claim was "retracted." Apple confirmed that it sent the original DMCA takedown request, and later asked Twitter to put the Tweet back online.

At the same time, Reddit received several DMCA takedown requests for posts on r/jailbreak, a popular subreddit where iPhone security researchers and hackers discuss techniques to jailbreak Apple devices, according to the subreddit's moderators. "Admins have not reached out to us in regards to these removals. We have no idea who is submitting these copyright claims," one moderator wrote.

Transportation

World's First Fully Electric Commercial Aircraft Takes Flight in Canada (theguardian.com) 208

The world's first fully electric commercial aircraft has taken its inaugural test flight, taking off from the Canadian city of Vancouver and flying for 15 minutes. From a report: "This proves that commercial aviation in all-electric form can work," said Roei Ganzarski, chief executive of Australian engineering firm magniX. The company designed the plane's motor and worked in partnership with Harbour Air, which ferries half a million passengers a year between Vancouver, Whistler ski resort and nearby islands and coastal communities. Ganzarski said the technology would mean significant cost savings for airlines and zero emissions. "This signifies the start of the electric aviation age," he said. Civil aviation is one of the fastest-growing sources of carbon emissions as people increasingly take to the skies, and new technologies have been slow to get off the ground. The International Civil Aviation Organization (ICAO) has encouraged greater use of efficient biofuel engines and lighter aircraft materials, as well as route optimization.
Youtube

YouTube Unveils a Stricter Harassment Policy (cnn.com) 152

After months of promising to reexamine how it handles harassment on its platform, YouTube has unveiled an update to its policy. From a report: On Wednesday, the Google-owned video platform said it would take a "stronger stance" against threats and personal attacks, among other changes intended to address the safety of its community. YouTube said it would now prohibit "veiled" or "implied" threats, not just explicit ones. This new policy includes content that simulates violence against a person or language indicating physical violence could occur. YouTube also said it will no longer permit "maliciously" insulting someone based on characteristics like race, gender expression or sexual orientation, whether it's a private individual, YouTube personality or public figure. The policy applies to content, as well as comments. The move comes six months after YouTube faced one of its most high-profile controversies over harassment in recent memory.
Transportation

Internal FAA Review Saw High Risk of 737 MAX Crashes (wsj.com) 38

U.S. regulators decided to allow Boeing's 737 MAX jet to keep flying after its first fatal crash last fall even after their own analysis indicated it could become one of the most accident-prone airliners in decades without design changes [Editor's link: the link may be paywalled], the Wall Street Journal reports. From the report: The November 2018 internal Federal Aviation Administration analysis, released during a House committee hearing Wednesday, reveals that without agency intervention, the MAX could have averaged one fatal crash about every two or three years. That amounts to a substantially greater safety risk than either Boeing or the agency indicated publicly at the time. The assessment, which came the month after a Lion Air crash in Indonesia, raises new questions about the FAA's decision-making in the wake of that disaster, along with what turned out to be faulty agency assumptions on ways to alleviate hazards.

In the wake of the analysis, the FAA took steps to put short-term and permanent measures in place to combat hazards, but Wednesday's hearing started off with challenges to some of those decisions. "Despite its own calculations, the FAA rolled the dice on the safety of the traveling public and let the 737 MAX continue to fly," said Rep. Peter DeFazio (D., Ore.), chairman of the House Transportation Committee. The FAA's intervention proved inadequate after a second fatal MAX crash, in Ethiopia in March, led to the global grounding of the fleet and sparked an international controversy over the agency's safety oversight.

Privacy

India Proposes New Rules To Access Its Citizens' Data (techcrunch.com) 14

India has proposed groundbreaking rules, akin to Europe's GDPR, that would require technology companies to garner consent from citizens before collecting and processing their personal data. But at the same time, the new rules also state that companies would have to hand over "non-personal" data of their users to the government, and New Delhi would also hold the power to collect any data of its citizens without consent to serve sovereignty and larger public interest. From a report: The new rules, proposed in nation's first major data protection law dubbed "Personal Data Protection Bill 2019," a copy of which leaked on Tuesday, would permit New Delhi to "exempt any agency of government from application of Act in the interest of sovereignty and integrity of India, the security of the state, friendly relations with foreign states, public order." If the bill passes select controversial laws drafted more than a decade ago would remain unchanged. The bill might also change how global technology companies that have invested billions of dollars in India, thanks in part to the lax laws, see the nation of more than 600 million internet users.
Twitter

Twitter Is Funding Independent Effort To Develop an Open and Decentralized Standard For Social Media (twitter.com) 58

Twitter is funding a small team of researchers to build an "open and decentralized standard for social media," with the goal of making Twitter a client for that standard. CEO Jack Dorsey announced the news and laid out his reasoning in a tweet thread this morning, although he acknowledged that the process could take years. The project is called Bluesky. Dorsey said: Twitter was so open early on that many saw its potential to be a decentralized internet standard, like SMTP (email protocol). For a variety of reasons, all reasonable at the time, we took a different path and increasingly centralized Twitter. But a lot's changed over the years. First, we're facing entirely new challenges centralized solutions are struggling to meet. For instance, centralized enforcement of global policy to address abuse and misleading information is unlikely to scale over the long-term without placing far too much burden on people. Second, the value of social media is shifting away from content hosting and removal, and towards recommendation algorithms directing one's attention. Unfortunately, these algorithms are typically proprietary, and one can't choose or build alternatives. Yet. Third, existing social media incentives frequently lead to attention being focused on content and conversation that sparks controversy and outrage, rather than conversation which informs and promotes health. Finally, new technologies have emerged to make a decentralized approach more viable. Blockchain points to a series of decentralized solutions for open and durable hosting, governance, and even monetization. Much work to be done, but the fundamentals are there. Twitter CTO Parag Agrawal is tasked with finding a lead for the project, who will build a team of up to five people. The Bluesky account's only tweet quotes Dorsey with the comment "lo" -- a reference to the first message ever sent on the internet.
Businesses

'Learning at Work is Work, and We Must Make Space For It' (mit.edu) 123

An anonymous reader shares a paper: The event was running over, the car was waiting, but the keynote speaker did not seem to mind. He was enjoying fielding questions from a large auditorium packed to the rafters with executives, aspiring entrepreneurs, and management students. "Get ready for an age in which we are all in tech," he had told them, "whether you work in the tech industry or not." The moderator called for one last question. "What's the best way to get ready?" a woman asked. "Be great at learning," he said without hesitation. "The moment you stop learning is the moment you begin to die." Calls for learning have long been common at corporate retreats, professional conferences, and similar gatherings. But with the furious pace of change that technology has brought to business and society, they have become more urgent.

Leaders in every sector seem to agree: Learning is an imperative, not a cliche. Without it, careers derail and companies fail. Talented people flock to employers that promise to invest in their development whether they will stay at the company or not. And companies spend heavily on it. By one estimate, in 2018, corporate outlays on learning and development initiatives topped $200 billion. Despite the lofty statements and steep investments, however, learning at work remains complicated. People are ambivalent about it, if not outright resistant. We want to learn, but we worry that we might not like what we learn. Or that learning will cost us too much. Or that we will have to give up cherished ideas. There is often some shame involved in learning something new as an adult, a mentor told me at the start of my career. What if, in the process, we're found lacking? What if we simply cannot pick up the knowledge and skills we need? I have spent two decades studying adult learning, helping companies design and deploy learning initiatives, and teaching and coaching thousands of high potentials and executives all over the world. And I have found that mentor's words to be wise: Nothing truly novel, nothing that matters, is ever learned with ease.

IBM

George Laurer, Co-Inventor of the Barcode, Dies At 94 (bbc.com) 21

An anonymous reader quotes a report from the BBC: George Laurer, the U.S. engineer who helped develop the barcode, has died at the age of 94. Barcodes, which are made up of black stripes of varying thickness and a 12-digit number, help identify products and transformed the world of retail. They are now found on products all over the world. The idea was pioneered by a fellow IBM employee, but it was not until Laurer developed a scanner that could read codes digitally that it took off. Laurer died last Thursday at his home in Wendell, North Carolina, and his funeral was held on Monday.

It was while working as an electrical engineer with IBM that George Laurer fully developed the Universal Product Code (UPC), or barcode. He developed a scanner that could read codes digitally. He also used stripes rather than circles that were not practical to print. The UPC went on to revolutionize "virtually every industry in the world", IBM said in a tribute on its website.

Links

The Pirate Bay Is Trialing High-Quality Video Streaming Links (torrentfreak.com) 35

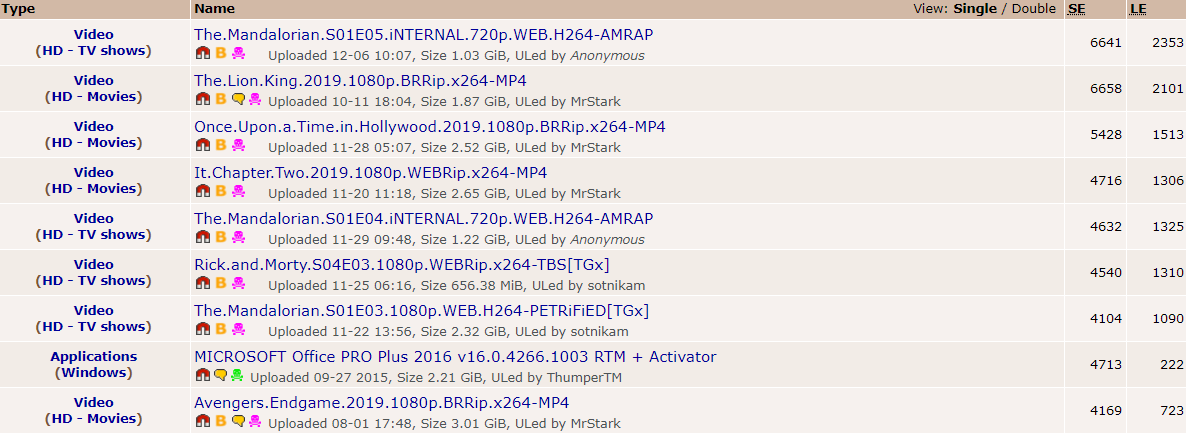
The Pirate Bay may be about to fully launch a brand new feature that will let you stream videos in your browser. TorrentFreak reports: As the image below shows, in addition to the familiar magnet and trusted uploader icons displayed alongside video and TV show releases, the site also features a small orange 'B' graphic. In some cases (but currently not all), pressing these buttons when they appear next to a video release diverts users to a new platform called BayStream. Here, the chosen content can be streamed directly in the browser using a YouTube-style player interface.

Loading times appear swift when the content is actually available and as the screenshot below shows, the material appears to be sourced, at least in some cases, from torrent releases. The new feature appears to be in its early stages of development and in tests doesn't always perform as planned. In particular, accessing the 'B' links using various Pirate Bay 'proxy' sites can cause them to break with various errors. Nevertheless, when things go to plan (usually when selecting more popular content) the system appears effective. [...] The big question, perhaps, is whether this is a Pirate Bay-operated platform or one run by outsiders. The familiar 'Kopimi' logo at the bottom suggests that it could be someone who supports the 'pirate' movement but anyone can use the image freely, so that's not the best pointer.

Software

Researchers Report Breakthrough In 'Distributed Deep Learning' (techxplore.com) 16

Using a divide-and-conquer approach that leverages the power of compressed sensing, computer scientists from Rice University and Amazon have shown they can slash the amount of time and computational resources it takes to train computers for product search and similar "extreme classification problems" like speech translation and answering general questions. Tech Xplore reports: In tests on an Amazon search dataset that included some 70 million queries and more than 49 million products, Shrivastava, Medini and colleagues showed their approach of using "merged-average classifiers via hashing," (MACH) required a fraction of the training resources of some state-of-the-art commercial systems. "Our training times are about 7-10 times faster, and our memory footprints are 2-4 times smaller than the best baseline performances of previously reported large-scale, distributed deep-learning systems," said Shrivastava, an assistant professor of computer science at Rice. Medini, a Ph.D. student at Rice, said product search is challenging, in part, because of the sheer number of products. "There are about 1 million English words, for example, but there are easily more than 100 million products online."

MACH takes a very different approach [than current training algorithms]. Shrivastava describes it with a thought experiment randomly dividing the 100 million products into three classes, which take the form of buckets. "I'm mixing, let's say, iPhones with chargers and T-shirts all in the same bucket," he said. "It's a drastic reduction from 100 million to three." In the thought experiment, the 100 million products are randomly sorted into three buckets in two different worlds, which means that products can wind up in different buckets in each world. A classifier is trained to assign searches to the buckets rather than the products inside them, meaning the classifier only needs to map a search to one of three classes of product. [...] In their experiments with Amazon's training database, Shrivastava, Medini and colleagues randomly divided the 49 million products into 10,000 classes, or buckets, and repeated the process 32 times. That reduced the number of parameters in the model from around 100 billion to 6.4 billion. And training the model took less time and less memory than some of the best reported training times on models with comparable parameters, including Google's Sparsely-Gated Mixture-of-Experts (MoE) model, Medini said. He said MACH's most significant feature is that it requires no communication between parallel processors. In the thought experiment, that is what's represented by the separate, independent worlds.
The research will be presented this week at the 2019 Conference on Neural Information Processing Systems (NeurIPS 2019) in Vancouver.
Businesses

Nikon Is Killing Its Authorized Repair Program (ifixit.com) 109

According to iFixit, Nikon is ending its authorized repair program next year, "likely leaving more than a dozen repair shops without access to official parts and tools, and cutting the number of places you can get your camera fixed with official parts from more than a dozen independent shops to two facilities at the ends of the U.S." From the report: That means that Nikon's roughly 15 remaining Authorized Repair Station members are about to become non-authorized repair shops. Since Nikon decided to stop selling genuine parts to non-authorized shops back in 2012, it's unlikely those stores will continue to have access to the specialty components, tools, software, manuals, and model training Nikon previously provided. But Nikon hasn't clarified this, so repair shops have been left in the dark.

In a letter obtained by iFixit, Nikon USA told its roughly 15 remaining Authorized Repair Station members in early November that it would not renew their agreements after March 31, 2020. The letter notes that "The climate in which we do business has evolved, and Nikon Inc. must do the same." And so, Nikon writes, it must "change the manner in which we make product service available to our end user customers." [...] In a statement, Nikon confirmed the termination of Authorized Repair Stations contracts after March 2020. Authorized service, Nikon stated, will be provided at its Melville, NY and Los Angeles, Calif. facilities. "We remain committed to providing the best product support and repair services to our customers," Nikon stated. Nikon did not answer our questions about the former authorized shops' access to parts or other official services.

Transportation

Vietnam's Richest Man Bets $2 Billion To Sell Cars To Americans (bloomberg.com) 77

An anonymous reader quotes a report from Bloomberg: The billionaire behind six-month-old Vietnamese auto startup VinFast plans a feat even Toyota and Hyundai couldn't pull off during their early days: sell a car in the U.S. Pham Nhat Vuong, the Southeast Asian country's richest man and now in charge of the new automaker, is so intent on exporting electric vehicles to the lucrative American market in 2021 that he's plowing as much as $2 billion of his own fortune to reach that goal. His cash would account for half the capital investment of VinFast, which began delivering cars to Vietnamese consumers with BMW-licensed engines earlier this year and aims to expand into electric vehicles.

"Our ultimate goal is to create an international brand," the 51-year-old tycoon said in an interview at the Hanoi headquarters of the car company's parent Vingroup JSC, which Vuong founded and holds the title of chairman. "It will be a very difficult road and we will have to put in a lot of effort. But there's only one road ahead." [...] The tycoon, whose net worth is $9.1 billion, according to the Bloomberg Billionaires Index, is undaunted. He sold some of his shares in Vingroup last year and plans to sell as much as 10% more to raise funds for the ambitious project. He owns 49% of VinFast, while the parent, Vingroup, holds 51%. [...] VinFast's first EV won't roll off its assembly line until late next year, but Vuong said he plans to export those vehicles to the U.S., Europe and Russia in 2021. VinFast, which operates a 335-hectare factory in the northern port city of Haiphong, is selling its first line of vehicles -- a hatchback, sedan and SUV -- at below cost. The hatchback retails for the equivalent of $17,000, while the four-cylinder sedan goes for $47,400 and its SUV is offered at $60,400. The company targets production of as many as 500,000 vehicles a year by 2025.

Chrome

Chrome Now Warns You When Your Password Has Been Stolen (theverge.com) 49

Google is rolling out Chrome 79, and it includes a number of password protection improvements. The Verge reports: The biggest addition is that Chrome will now warn you when your password has been stolen as part of a data breach. Google has been warning about reused passwords in a separate browser extension or in its password checkup tool, but the company is now baking this directly into Chrome to provide warnings as you log in to sites on the web.

You can control this new functionality in the sync settings in Chrome, and Google is using strongly hashed and encrypted copies of passwords to match them using multiple layers of encryption. This allows Google to securely match passwords using a technique called private set intersection with blinding. Alongside password warnings, Google is also improving its phishing protection with a real-time option. Google has been using a list of phishing sites that updates every 30 minutes, but the company found that fraudsters have been quickly switching domains or hiding from Google's crawlers. This new real-time protection should generate warnings for 30 percent more cases of phishing.

Facebook

Facebook Fired a Contractor Who Was Paid Thousands In Bribes To Reactivate Banned Ad Accounts (buzzfeednews.com) 21

BuzzFeed News has found that a Facebook contractor was paid thousands of dollars in bribes by a shady affiliate marketer to reactivate ad accounts that had been banned due to policy violations. From the report: A company spokesperson confirmed that an unnamed worker was fired after inquiries from BuzzFeed News sparked an internal investigation. The person in question was based in the company's Austin office, according to information obtained by BuzzFeed News. The individual was paid to reactivate ad accounts connected to Ads Inc., a San Diego-based marketing firm BuzzFeed News previously revealed was running a sophisticated Facebook scam that involved placing more than $50 million in ads that typically made false claims about celebrities. The ads were part of a scheme that tricked consumers into signing up for an expensive monthly subscription for a product that was initially marketed as a free trial. Ads Inc. announced it was shutting down in October as a result of the BuzzFeed News investigation.

Chat messages obtained by BuzzFeed News, as well as information from former Ads Inc. employees, show how former Ads Inc. CEO Asher Burke and the Facebook insider conspired to reactivate banned ad accounts, further exposing Facebook users to scams by pitching dubious products. A former Ads Inc. employee told BuzzFeed the company had more than one person inside Facebook who would turn ads back on for a fee. "To be honest there were a few people that would flip ads back on," they told BuzzFeed News. They said that the Facebook mole (or moles) wouldn't receive their money if the reactivated ads didn't run for at least two days. Facebook declined to comment on whether it suspects others helped reactivate ads but said its investigation is ongoing.
"This behavior is absolutely prohibited under our policies and the individual is no longer working with Facebook," a Facebook spokesperson said in an emailed statement. "We're continuing to investigate the allegations and will take any further necessary action."
Security

New Plundervolt Attack Impacts Intel Desktop, Server, and Mobile CPUs (zdnet.com) 74

An anonymous reader quotes a report from ZDNet: Academics from three universities across Europe have disclosed today a new attack that impacts the integrity of data stored inside Intel SGX, a highly-secured area of Intel CPUs. The attack, which researchers have named Plundervolt, exploits the interface through which an operating system can control an Intel processor's voltage and frequency -- the same interface that allows gamers to overclock their CPUs. Academics say they discovered that by tinkering with the amount of voltage and frequency a CPU receives, they can alter bits inside SGX to cause errors that can be exploited at a later point after the data has left the security of the SGX enclave. They say Plundervolt can be used to recover encryption keys or introduce bugs in previously secure software. Intel desktop, server, and mobile CPUs are impacted. A full list of vulnerable CPUs is available here. Intel has also released microcode (CPU firmware) and BIOS updates today that address the Plundervolt attack [by allowing users to disable the energy management interface at the source of the attack, if not needed]. Proof-of-concept code for reproducing attacks will be released on GitHub.
Censorship

Iran's Internet Freedom is On Life Support (cnet.com) 60

An anonymous reader shares a report: In November, Iran's government announced a price hike on oil, leading to mass protests in Tehran. To quell the spreading unrest, the Iranian government effectively shut down the internet. After a week of Iranian security forces cracking down on protesters, including an estimated death toll between 140 and 208, internet access was gradually restored around the country. Judging by statements made by President Hassan Rouhani, the internet shutdowns could be a harbinger of more censorship in 2020 and beyond. Iran's intranet, known as the National Information Network, will be expanded so "people will not need foreign [networks] to meet their needs," President Rouhani said to Iran's parliament on Sunday, according to Radio Farda. The decree to bolster the NIN comes from Supreme Leader Ali Khamenei himself, Rouhani said. Developing a more robust intranet would allow the Iranian government to cut access to the internet, and Iranians off from the rest of the world, without the economic self-impairment that internet cutoffs cause. An intranet would allow the Iranian government to select what sites and content Iranians can see, as opposed to the blunt and costly tool of a total shutdown.

Slashdot Top Deals