Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
CanditechCanditech empowers HR professionals and hiring managers to make fast, confident and objective hiring decisions. It's all-in-one testing platform evaluates both technical and soft skills through job simulation assessments that cover a variety of tasks, including coding, SQL, Excel, open text, email communication, and video. These tests are the best predictors of future job suitability and performance. The platform's holistic approach allows recruiters and hiring managers the ability to objectively assess candidates for any position within the company (R&D and Data, Marketing, Sales and Customer Success, Technical Support, Technical Support, etc.). You can also assess your technical skills (codes, SQL, Excel, etc.). Along with soft skills (using video questions and email communication), it gives candidates a fair chance of showcasing their talents, creating a great candidate experience. The platform offers significant ROI from day one: ✅ Shorten time-to-hire by 50% ✅ Reduce unnecessary interviews by 80% ✅ Increase hiring diversity and eliminate bias
-
Astra PentestAstra's Pentest is a comprehensive solution for penetration testing. It includes an intelligent vulnerability scanner and in-depth manual pentesting. The automated scanner performs 10000+ security checks, including security checks for all CVEs listed in the OWASP top 10 and SANS 25. It also conducts all required tests to comply with ISO 27001 and HIPAA. Astra provides an interactive pentest dashboard which allows users to visualize vulnerability analysis, assign vulnerabilities to team members, collaborate with security experts, and to collaborate with security experts. The integrations with CI/CD platforms and Jira are also available if users don't wish to return to the dashboard each time they want to use it or assign a vulnerability for a team member.
-
Nexcess Digital CloudNexcess Digital Cloud functions as a managed hosting and cloud infrastructure provider, dedicated to offering dependable, secure, and high-performance hosting services tailored for businesses across various sizes. Their extensive range of offerings encompasses managed dedicated servers, cloud dedicated hosting, managed VPS hosting, along with specialized environments for WordPress, WooCommerce, and Magento. Aimed at organizations that demand exceptional uptime and expert assistance, Nexcess Digital Cloud integrates enterprise-grade infrastructure with fully managed services, ensuring proactive technical support is always available. Their hosting solutions are meticulously engineered for performance, security, scalability, and uninterrupted business operations, allowing clients to concentrate on their growth rather than server management. Furthermore, customers benefit from a dedicated team of hosting professionals who are on hand 24/7 to provide help with deployment, maintenance, troubleshooting, and optimization, ensuring a seamless experience. This commitment to service excellence sets Nexcess apart in the competitive landscape of digital solutions.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Nutrient SDKNutrient provides an extensive solution for all your PDF requirements, delivering tools that seamlessly operate PDF features across any platform. 1. SDK: Incorporate advanced PDF functionality into iOS, Android, Windows, web, or any cross-platform technology, supplying abilities like PDF viewing, annotation, collaboration, and beyond. 2. Libraries: Employ our powerful .NET and Java libraries to enhance your backend applications with batch processing of redactions and PDF forms, OCR'd scanned text, and PDF document editing, all directly from your application server. 3. Processor: Our agile PDF microservice, Processor, enables rapid generation of PDFs from HTML, including HTML forms, as well as Office-to-PDF conversions, OCR, redaction, and XFDF combining and exporting. 4. PDF API: Take advantage of our hosted PDF API to generate, convert, and alter PDF documents in your workflows. We handle the development and server management, freeing you up to concentrate on your business. At Nutrient, we're not just a tool; we're a committed ally in your success. Gain direct contact with our engineers for expert guidance, utilize comprehensive examples to simplify integration, and make the most of our top-tier documentation.
-
ParasoftParasoft's mission is to provide automated testing solutions and expertise that empower organizations to expedite delivery of safe and reliable software. A powerful unified C and C++ test automation solution for static analysis, unit testing and structural code coverage, Parasoft C/C++test helps satisfy compliance with industry functional safety and security requirements for embedded software systems.
-
SurveyJSSurveyJS is a set of four open-source JavaScript libraries that offer the benefits of a tailor-made in-house survey application, while considerably reducing the time and resources needed to deploy the system. These libraries are independent of specific server code or database requirements and seamlessly integrate with popular JavaScript frameworks, including React, Angular, Vue.js, jQuery, Knockout, and more. They are designed to communicate with any server that can handle JSON requests, ensuring compatibility with various server architectures and databases. The product family is composed of: - An open-source MIT-licensed rendering library that renders dynamic JSON-based forms in your web application, and collects responses. - A self-hosted drag & drop form builder that features an integrated CSS-based theme editor and a GUI for conditional rules. It automatically generates JSON definitions (schemas) of your forms in real time. - PDF Generator, a library that renders SurveyJS surveys and forms as PDF files in a browser; - The Dashboard library that allows you to simplify survey data analysis with interactive and customizable charts and tables. Visit our website to try out and evaluate our full-scale demo for free.
Description
OpenText Dynamic Application Security Testing (DAST) offers enterprises a powerful, automated way to detect real-world security vulnerabilities by simulating live attacks against running applications, APIs, and services without requiring access to source code or staging environments. Tailored for DevSecOps teams, it efficiently prioritizes security issues to enable root cause analysis and faster remediation. The platform integrates effortlessly via REST APIs and features a user-friendly dashboard, supporting fully automated workflows within CI/CD pipelines for continuous security testing. OpenText DAST accelerates vulnerability discovery by tuning scans to the application environment, reducing false positives and surfacing critical risks earlier in the software development lifecycle. It supports modern web technologies including HTML5, JSON, AJAX, JavaScript, and HTTP2 to provide broad coverage across today’s digital applications. Automated features like macro generation and redundant page detection boost testing efficiency and reduce manual work. The solution offers flexible deployment choices, allowing organizations to operate on public or private clouds or on-premises systems. Backed by expert professional services, OpenText DAST helps businesses secure their software supply chains and maintain application integrity at scale.
Description
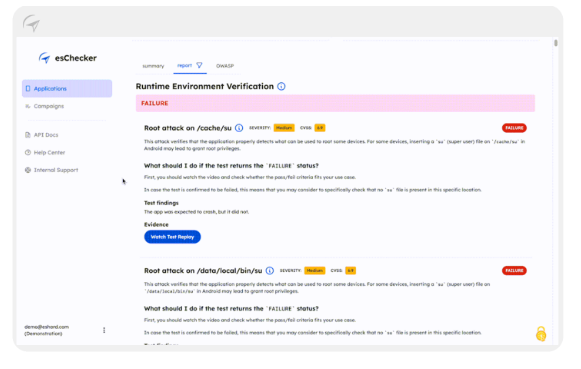
With esChecker, you can accelerate your release cycles, significantly cut down on testing and delivery expenses, and reduce potential risks. Don't sacrifice your digital transformation; instead, enhance the security of your mobile applications through automated testing seamlessly integrated into your CI/CD pipeline. Featuring a distinctive dynamic analysis capability, esChecker runs the mobile application binary on compromised devices, providing prompt insights into your security measures. Just like any integral IT system component, mobile applications must be thoughtfully designed, developed, and maintained with security as a priority, as they serve as critical gateways to the overall system. Given their importance, they warrant careful scrutiny. In contrast to traditional pentesting, a Mobile Application Security Testing (MAST) tool offers a faster, more streamlined, and effective approach to security testing, allowing for better management of the application's code throughout its development. This process focuses on code validation that is woven into the development cycle, delivering immediate feedback, ensuring compliance, and fitting seamlessly into a DevSecOps framework, thereby enhancing overall application security. By prioritizing security during the development phase, organizations can build more resilient mobile applications that meet modern security challenges.
API Access
Has API
Yes
API Access
Has API
No


Integrations
Android
No
Apple iOS
No
ArmorCode
Yes
Azure DevOps
No
Bitrise
No
Bizzy
Yes
CircleCI
No
Clarive
Yes
Codemagic
No
Conviso Platform
Yes
Integrations
Android
Yes
Apple iOS
Yes
ArmorCode
No
Azure DevOps
Yes
Bitrise
Yes
Bizzy
No
CircleCI
Yes
Clarive
No
Codemagic
Yes
Conviso Platform
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Pricing Details
Free
Free Trial
No
Free Version
Yes
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
Yes
Online Support
Yes
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
No
In Person
Yes
Vendor Details
Company Name
OpenText
Founded
1991
Country
Canada
Website
www.opentext.com/products/dynamic-application-security-testing
Vendor Details
Company Name
eShard
Country
France
Website
eshard.com/eschecker
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
