Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
GearsetGearset is a full‑featured Salesforce DevOps solution built for the enterprise, giving teams the tools to adopt best practices across every stage of the DevOps lifecycle. From metadata and CPQ deployments to CI/CD, testing, code analysis, sandbox seeding, backups, archiving, and observability, Gearset gives teams unmatched insight and control over their Salesforce workflows. Over 3,000 organizations — including names like McKesson and IBM — rely on Gearset to deliver with security and scale in mind. With advanced governance, detailed audit trails, SOX/ISO/HIPAA support, multi‑team pipelines, integrated security checks, and adherence to ISO 27001, SOC 2, GDPR, CCPA/CPRA, and HIPAA, Gearset combines enterprise‑ready compliance with rapid onboarding and an intuitive interface — all in one platform. Leading firms in finance, healthcare, and tech trust Gearset to power their DevOps initiatives without adding complexity.
-
Keeper SecurityPassword security is the foundation of cybersecurity. Keeper's powerful password security platform will protect your business from cyberthreats and data breaches related to passwords. Research shows that 81% of data breaches can be attributed to weak passwords. Password security platforms are an affordable and easy way for companies to address the root cause of most data breaches. Your business can significantly reduce the risk of data breaches by implementing Keeper. Keeper creates strong passwords for all websites and apps, then secures them on all devices. Each employee receives a private vault to store and manage their passwords, credentials and files, as well as private client data. Employees will save time and frustration by not having to remember, reset, reuse, or remember passwords. Industry compliance is achieved through strict and customizable role-based access controls. This includes 2FA, usage auditing, and event reporting.
-
Kasm WorkspacesKasm Workspaces streams your workplace environment directly to your web browser…on any device and from any location. Kasm is revolutionizing the way businesses deliver digital workspaces. We use our open-source web native container streaming technology to create a modern devops delivery of Desktop as a Service, application streaming, and browser isolation. Kasm is more than a service. It is a platform that is highly configurable and has a robust API that can be customized to your needs at any scale. Workspaces can be deployed wherever the work is. It can be deployed on-premise (including Air-Gapped Networks), in the cloud (Public and Private), or in a hybrid.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
JS7 JobSchedulerJS7 JobScheduler, an Open Source Workload Automation System, is designed for performance and resilience. JS7 implements state-of-the-art security standards. It offers unlimited performance for parallel executions of jobs and workflows. JS7 provides cross-platform job execution and managed file transfer. It supports complex dependencies without the need for coding. The JS7 REST-API allows automation of inventory management and job control. JS7 can operate thousands of Agents across any platform in parallel. Platforms - Cloud scheduling for Docker®, OpenShift®, Kubernetes® etc. - True multi-platform scheduling on premises, for Windows®, Linux®, AIX®, Solaris®, macOS® etc. - Hybrid cloud and on-premises use User Interface - Modern GUI with no-code approach for inventory management, monitoring, and control using web browsers - Near-real-time information provides immediate visibility to status changes, log outputs of jobs and workflows. - Multi-client functionality, role-based access management - OIDC authentication and LDAP integration High Availability - Redundancy & Resilience based on asynchronous design and autonomous Agents - Clustering of all JS7 Products, automatic fail-over and manual switch-over
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
-
MaintainlyMaintainly is a cloud-hosted maintenance management solution that streamlines both proactive and reactive maintenance processes. This software enables users to generate, assign, and oversee work orders, offering features such as photo uploads, meter readings, downtime monitoring, and comprehensive audit trails, which can be handled either manually or through automated preventive schedules. Users can organize assets in a hierarchical manner, track movable equipment geographically, and utilize QR codes for easy access, while every maintenance activity is recorded in a detailed history log. Teams and technicians benefit from push notifications, and maintenance personnel can receive and monitor requests using a mobile application that includes functionalities for on-site updates, task comments, and tracking time spent on jobs. Maintainly also offers customizable hierarchy configurations, sophisticated filtering options, and role-specific views, enabling complex operations across various industries to expand efficiently. With a focus on user-friendly adoption, the platform boasts a quick setup process, scalable modular features, and an intuitive design that enhances the user experience. This combination of capabilities makes Maintainly a versatile tool for managing maintenance tasks effectively.
Description
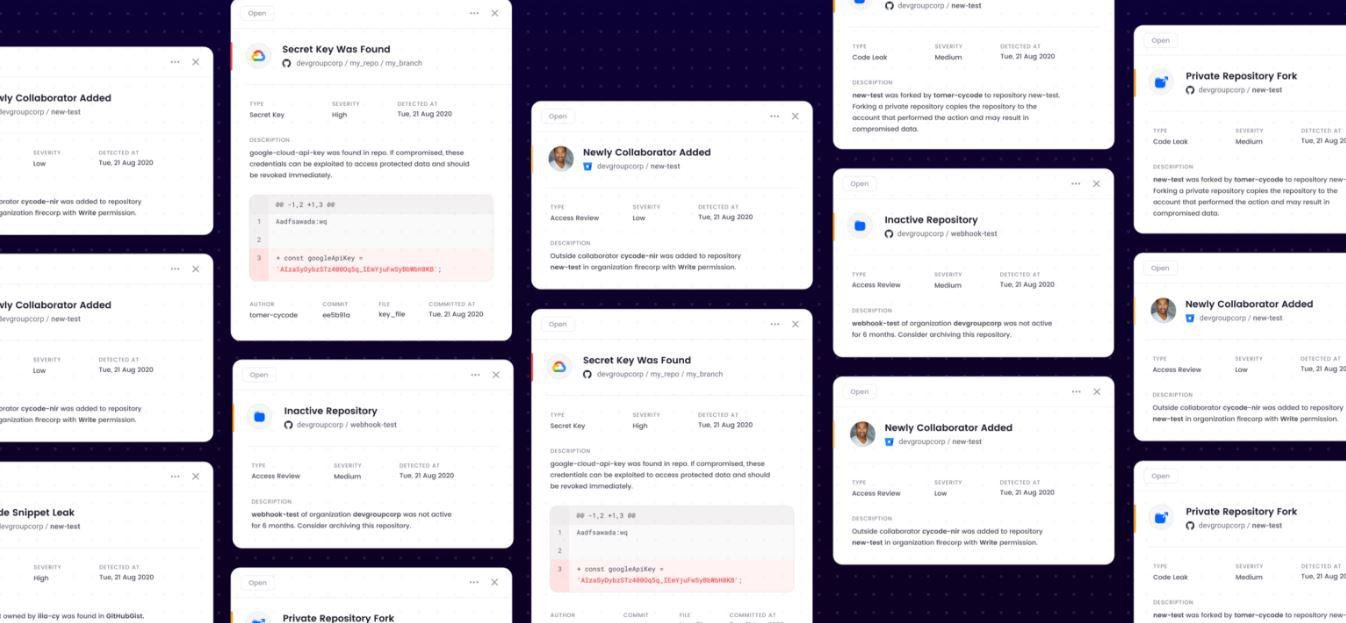
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
Description
Our advanced security solutions safeguard applications against reverse engineering, tampering, API vulnerabilities, and various other threats that could jeopardize your enterprise, your clientele, and your profitability. By obfuscating source code, incorporating honeypots, and employing various misleading coding techniques, we effectively deter and confound potential attackers. Additionally, our system activates defensive protocols automatically upon detecting any suspicious behavior, which may include shutting down the application, isolating users, or initiating self-repair of the code. We seamlessly integrate vital application protection measures and threat detection tools into the continuous integration and continuous deployment (CI/CD) pipeline after code development, ensuring that the DevOps workflow remains unperturbed. Furthermore, our technology encrypts both static and dynamic keys as well as sensitive data nestled within application code. It also secures sensitive information, whether at rest within the application or during transmission between the app and server. Our solutions are compatible with all leading cryptographic algorithms and modes, holding FIPS 140-2 certification to guarantee compliance and security standards. In an era where digital threats are increasingly sophisticated, our comprehensive approach ensures that your applications remain resilient and secure.
API Access
Has API
No
API Access
Has API
No




Integrations
Amazon Web Services (AWS)
Yes
Axonius
Yes
BMC Middleware Management
No
CircleCI
Yes
Cobalt
Yes
Databricks
Yes
Flexport
Yes
GitHub
Yes
Google Cloud Platform
Yes
Grubhub
Yes
Integrations
Amazon Web Services (AWS)
No
Axonius
No
BMC Middleware Management
Yes
CircleCI
No
Cobalt
No
Databricks
No
Flexport
No
GitHub
No
Google Cloud Platform
No
Grubhub
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
No
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
Yes
Mac
Yes
Linux
Yes
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Vendor Details
Company Name
Digital.ai
Country
United States
Website
digital.ai/application-protection
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
