Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
TrustInSoft AnalyzerTrustInSoft commercializes a source code analyzer called TrustInSoft Analyzer, which analyzes C and C++ code and mathematically guarantees the absence of defects, immunity of software components to the most common security flaws, and compliance with a specification. The technology is recognized by U.S. federal agency the National Institute of Standards and Technology (NIST), and was the first in the world to meet NIST’s SATE V Ockham Criteria for high quality software. The key differentiator for TrustInSoft Analyzer is its use of mathematical approaches called formal methods, which allow for an exhaustive analysis to find all the vulnerabilities or runtime errors and only raises true alarms. Companies who use TrustInSoft Analyzer reduce their verification costs by 4, efforts in bug detection by 40, and obtain an irrefutable proof that their software is safe and secure. The experts at TrustInSoft can also assist clients in training, support and additional services.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
ParasoftParasoft's mission is to provide automated testing solutions and expertise that empower organizations to expedite delivery of safe and reliable software. A powerful unified C and C++ test automation solution for static analysis, unit testing and structural code coverage, Parasoft C/C++test helps satisfy compliance with industry functional safety and security requirements for embedded software systems.
-
Source DefenseSource Defense is an essential element of web safety that protects data at the point where it is entered. Source Defense Platform is a simple, yet effective solution to data security and privacy compliance. It addresses threats and risks that arise from the increased use JavaScript, third party vendors, and open source code in your web properties. The Platform offers options for securing code as well as addressing an ubiquitous gap in managing third-party digital supply chains risk - controlling actions of third-party, forth-party and nth-party JavaScript that powers your website experience. Source Defense Platform provides protection against all types of client-side security incidents, including keylogging, formjacking and digital skimming. Magecart is also protected. - by extending the web security beyond the browser to the server.
-
ManageEngine Endpoint CentralManageEngine Endpoint Central is a unified endpoint management and security platform designed for IT teams managing diverse and distributed device environments eliminating the need for multiple disconnected products for patching, remote access, mobile management, and security. The platform supports Windows, macOS, Linux, iOS, Android, and Chrome OS. Automated patch deployment covers OS and 1,000+ third-party applications with scheduling, testing, rollback, and compliance reporting. Software can be deployed, updated, or removed across thousands of endpoints simultaneously. OS imaging workflows provision new devices quickly, while continuous asset inventory supports license compliance and audit readiness. Security capabilities are built directly into the platform. Vulnerability assessment identifies and prioritizes endpoint weaknesses by severity. Application control prevents unauthorized software execution. Device control governs USB and peripheral access. Endpoint privilege management removes unnecessary admin rights. EDR delivers behavioral threat detection and incident response, while NGAV blocks malware, ransomware, and zero-day threats. BitLocker and FileVault encryption enforces disk protection across Windows and macOS. Built-in remote desktop allows technicians to connect instantly without third-party software. Integrated MDM covers iOS and Android enrollment, app management, and remote wipe for corporate and BYOD environments. DEX monitoring gives IT teams real-time visibility into device performance enabling proactive issue resolution before productivity is impacted. Available as cloud or on-premises across Free, Professional, Enterprise, UEM, and Security editions.
-
DocmosisDocmosis is a self-hosted or SaaS template-based document generation solution. Integrate with custom-built software applications or popular third-party apps using the API. Create templates using MS Word or LibreOffice. Add plain-text placeholders to control: the insertion of text/images/tables; conditionally add/remove any content; perform calculations; loop over repeating data; format data/numbers and much more. Integrate with: Custom software built using Java, C#, Python, PHP, Ruby and more via a REST API; Low-code and no-code platforms like Appian, Bubble, Mendix, Outsystems; Third-party form builders or apps that can perform a webhook such as FormAssembly or Salesforce. Used by customers in Finance, Health, Legal, Education, Government, HR, Insurance, Logistics, and Manufacturing to generate customized letters invoices, proposals, contracts, statements, reports and more.
-
Gemini Enterprise Agent PlatformGemini Enterprise Agent Platform is Google Cloud’s next-generation system for designing and managing advanced AI agents across the enterprise. Built as the successor to Vertex AI, it unifies model selection, development, and deployment into a single scalable environment. The platform supports a vast ecosystem of over 200 AI models, including Google’s latest Gemini innovations and popular third-party models. It offers flexible development tools like Agent Studio for visual workflows and the Agent Development Kit for deeper customization. Businesses can deploy agents that operate continuously, maintain long-term memory, and handle multi-step processes with high efficiency. Security and governance are central, with features such as agent identity verification, centralized registries, and controlled access through gateways. The platform also enables seamless integration with enterprise systems, allowing agents to interact with data, applications, and workflows securely. Advanced monitoring tools provide real-time insights into agent behavior and performance. Optimization features help refine agent logic and improve accuracy over time. By combining automation, intelligence, and governance, the platform helps organizations transition to autonomous, AI-driven operations. It ultimately supports faster innovation while maintaining enterprise-grade reliability and control.
Description
DerScanner is a user-friendly, officially CWE-Compatible tool that integrates the functionalities of static application security testing (SAST), dynamic application security testing (DAST), and software composition analysis (SCA) within a single platform. This solution significantly enhances oversight of application and information system security, allowing users to assess both proprietary and open-source code seamlessly. By correlating findings from SAST and DAST, it enables the verification and prioritization of vulnerability remediation. Users can bolster their code integrity by addressing weaknesses in both their own and third-party software components. Moreover, it facilitates an impartial code review process through application analysis that is independent of developers. This tool effectively identifies vulnerabilities and undocumented features throughout all phases of the software development lifecycle. Additionally, it allows for oversight of both in-house and external developers while ensuring the security of legacy applications. Ultimately, DerScanner aims to improve user experience by delivering a well-functioning and secure application that meets modern security demands. With its comprehensive approach, organizations can feel confident in their software's resilience against threats.
Description
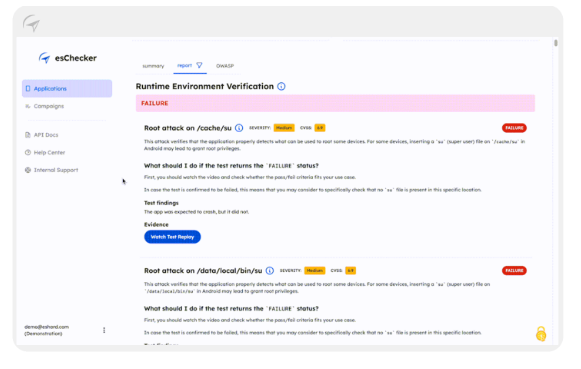
With esChecker, you can accelerate your release cycles, significantly cut down on testing and delivery expenses, and reduce potential risks. Don't sacrifice your digital transformation; instead, enhance the security of your mobile applications through automated testing seamlessly integrated into your CI/CD pipeline. Featuring a distinctive dynamic analysis capability, esChecker runs the mobile application binary on compromised devices, providing prompt insights into your security measures. Just like any integral IT system component, mobile applications must be thoughtfully designed, developed, and maintained with security as a priority, as they serve as critical gateways to the overall system. Given their importance, they warrant careful scrutiny. In contrast to traditional pentesting, a Mobile Application Security Testing (MAST) tool offers a faster, more streamlined, and effective approach to security testing, allowing for better management of the application's code throughout its development. This process focuses on code validation that is woven into the development cycle, delivering immediate feedback, ensuring compliance, and fitting seamlessly into a DevSecOps framework, thereby enhancing overall application security. By prioritizing security during the development phase, organizations can build more resilient mobile applications that meet modern security challenges.
API Access
Has API
No
API Access
Has API
No
Screenshots View All
No images available

Integrations
Android
No
Apple iOS
No
Azure DevOps
No
Bitrise
No
CircleCI
No
Codemagic
No
GitHub
No
GitLab
No
Jenkins
No
OWASP Threat Dragon
No
Integrations
Android
Yes
Apple iOS
Yes
Azure DevOps
Yes
Bitrise
Yes
CircleCI
Yes
Codemagic
Yes
GitHub
Yes
GitLab
Yes
Jenkins
Yes
OWASP Threat Dragon
Yes
Pricing Details
$500 USD
Free Trial
Yes
Free Version
No
Pricing Details
Free
Free Trial
No
Free Version
Yes
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
Yes
Mac
Yes
Linux
Yes
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
No
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
Yes
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
No
In Person
Yes
Vendor Details
Company Name
DerSecur
Founded
2011
Country
Israel
Website
derscanner.com
Vendor Details
Company Name
eShard
Country
France
Website
eshard.com/eschecker
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Static Application Security Testing (SAST)
Application Security
No
Dashboard
No
Debugging
No
Deployment Management
No
IDE
No
Multi-Language Scanning
No
Real-Time Analytics
No
Source Code Scanning
No
Vulnerability Scanning
No
