Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
ParasoftParasoft's mission is to provide automated testing solutions and expertise that empower organizations to expedite delivery of safe and reliable software. A powerful unified C and C++ test automation solution for static analysis, unit testing and structural code coverage, Parasoft C/C++test helps satisfy compliance with industry functional safety and security requirements for embedded software systems.
-
TrustInSoft AnalyzerTrustInSoft commercializes a source code analyzer called TrustInSoft Analyzer, which analyzes C and C++ code and mathematically guarantees the absence of defects, immunity of software components to the most common security flaws, and compliance with a specification. The technology is recognized by U.S. federal agency the National Institute of Standards and Technology (NIST), and was the first in the world to meet NIST’s SATE V Ockham Criteria for high quality software. The key differentiator for TrustInSoft Analyzer is its use of mathematical approaches called formal methods, which allow for an exhaustive analysis to find all the vulnerabilities or runtime errors and only raises true alarms. Companies who use TrustInSoft Analyzer reduce their verification costs by 4, efforts in bug detection by 40, and obtain an irrefutable proof that their software is safe and secure. The experts at TrustInSoft can also assist clients in training, support and additional services.
-
FinOpslyMost enterprises can report what AI cost them. Far fewer can say which team owns it, whether it was approved, or what it returned. FinOpsly closes that gap. The platform governs AI spend on the same cost model that carries the cloud, data platform and SaaS an AI workload consumes, so a business unit sees the full cost of an AI initiative instead of four disconnected bills. Capabilities include: Cost estimation before deployment. Model an architecture and get a priced workload across model APIs, GPU capacity, warehouse consumption and storage, with the assumptions on screen. Weigh model choices against consumption you have actually measured. Attribution that holds up in a chargeback cycle. Spend resolves to owners, teams, applications, business units and customers through hierarchies nine or more levels deep. Tagging is standardized across providers, keys and resources are labeled in bulk from plain-language rules, and whatever remains unattributed is published as a number, not absorbed. Guardrails that act. Set budgets by project, team or API key. Catch anomalies with root cause and route them to whoever owns the resource. Surface waste that provider tooling misses, using FinOpsly's own detection models. Plan commitments across AWS, Azure and Google Cloud. Park idle compute on approved schedules, reversibly. Financial results you can defend. Automated chargeback in a single cycle. Savings measured as what reached run-rate against a no-action baseline. Unit economics down to cost per call, per active user and per customer served. For technology and finance leaders accountable for what AI spend returns.
-
Captain ComplianceCaptain Compliance is a privacy management platform that simplifies compliance with global data protection legislation and new AI regulatory requirements. Our Consent Management Platform allows businesses to easily manage user consent, and create customized cookie banners. Our advanced Cookie Scanner automatically detects and categorizes all cookies on your site, ensuring compliance with a dynamic policy. Our DSAR Portal streamlines requests from data subjects, while our AI Compliance Tool monitors and adapts to evolving regulations. We even offer a virtual DPO or CPO if data privacy guidance is needed. Our Hosted Privacy Policy Generator automatically updates your privacy policies in real-time to ensure that they are always up-to date with the latest legal requirements. Captain Compliance offers you the tools to maintain regulatory compliance and protect user data at an affordable price.
-
ManageEngine ADAudit PlusADAudit Plus enhances the security and compliance of your Windows Server environment by delivering comprehensive insights into all operational activities. It offers a detailed overview of modifications made to Active Directory (AD) resources, encompassing AD objects and their respective attributes, group policies, and more. By conducting thorough AD audits, organizations can identify and mitigate insider threats, misuse of privileges, and other signs of potential security breaches, thereby bolstering their overall security framework. The tool enables users to monitor intricate details within AD, including entities such as users, computers, groups, organizational units (OUs), group policy objects (GPOs), schemas, and sites, along with their associated attributes. Furthermore, it tracks user management activities like the creation, deletion, password resets, and alterations in permissions, providing insights into the actions taken, the responsible individuals, the timing, and the originating locations. Additionally, it allows organizations to monitor the addition or removal of users from security and distribution groups, ensuring that access privileges are kept to the necessary minimum, which is critical for maintaining a secure environment. This level of oversight is vital for proactive security management and compliance adherence.
-
MedTrainerMedTrainer accelerates and simplifies healthcare workforce education, compliance, and credentialing. MedTrainer’s natively built software platform provides a seamless user experience that helps healthcare organizations thrive in managing their workforce. Learning: A healthcare-specific learning management system (LMS) enriched with thousands of education courses and resources created by subject matter experts to satisfy regulatory, accreditation requirements, and provide continuing education credit. Compliance: A technology solution that combines incident reporting, document, and policy management, and highly customizable reports to improve compliance. Credentialing: An end-to-end credentialing capability with automation, workflows, and centralized data to simplify the process and reduce costly delays. From PSV to provider enrollment and privileging, everything is in one platform with complete visibility.
-
ManageEngine ADSelfService PlusBoth IT teams and end users are afflicted by password reset tickets. IT teams will often push more urgent issues down the queue to ensure that users don't have their work put on hold while their passwords reset. Password reset tickets can be costly if they aren't addressed promptly. Nearly 30 percent of all help desk tickets were caused by forgotten passwords. It is not surprising that large companies have spent more than $1 million to resolve password-related help desk requests. It is a good habit to change passwords regularly, as it helps prevent cyberattacks caused by stolen credentials. Security experts recommend that administrators ensure that users change their passwords regularly and have password expiration policies in place.
-
InfoBoxEliminate communication silos and simplify enterprise content delivery across your entire workforce. InfoBox provides IT and corporate communications teams with a secure, centralized hub for broadcasting updates, standard operating procedures (SOPs), and operational resources. Designed to overcome the low engagement of legacy intranets and messy email threads, InfoBox pushes targeted updates directly to mobile devices, web applications, and desktop email clients. Core Technical & Platform Capabilities: 1. Granular Role-Based Access & Segmentation: Categorize content delivery by department, location, role, or administrative unit to ensure users receive strictly relevant information. 2. Flexible Authentication & External Access: Support for multi-provider authentication (Google Workspace, Microsoft 365, Yahoo, and personal email accounts) enables secure inclusion of contractors, frontline workers, and external partners without requiring additional core directory domain licenses. 3. Google Workspace /Microsoft 365: Native add-on integration allows users to consume visual updates and company feeds directly inside without additional costs. 4. Cross-Platform Accessibility: Native mobile clients for iOS and Android alongside a unified Web portal (infobox.info) ensure consistent UI/UX across all endpoint devices. 5. No-Code Content Builder & Resource Management: Equips administrators with visual templates for broadcasting policy updates, announcements, and searchable document libraries without IT intervention. 6. Engagement & Usage Analytics: Gain visibility into reach, content consumption, and search trends across the organization.
-
MobiPDFMobiPDF (formerly PDF Extra) is an intuitive reader and editor that allows you to read, edit, create, OCR, organize, annotate, fill and sign, convert, and share any PDF. This makes MobiPDF an excellent choice for users seeking a budget-friendly alternative to Adobe Acrobat Pro. HERE’S WHAT YOU GET WITH MOBIPDF: Multiple Page View Modes: Enjoy a distraction-free "Read Mode". Advanced Editing Tools: Experience a Word-like PDF editing environment. Two-Way Conversions: Convert PDFs to and from Word, Excel, PowerPoint, or image formats. OCR Support: Make scanned documents searchable. Markup Tools: Highlight, comment, strikethrough, stamp, and more to enhance your documents. Effortless PDF Organizer: Reorder, compress, split, and combine PDFs with ease. Sign & Secure: Add signatures, create and fill forms, and protect your PDFs with passwords, encryption, and digital certificates. Offline Mode: Work freely on your projects, even offline. Seamless translation: One-click translate any PDF into 50+ languages.
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
Description
Validate modifications across numerous supported resource types in all leading cloud service providers. Conduct scans of cloud resources during the build phase to identify misconfigured settings using a straightforward Python policy-as-code framework. Examine the connections between cloud resources through Checkov’s graph-oriented YAML policies. Run, test, and adjust runner parameters within the context of a specific repository's CI/CD processes and version control systems. Customize Checkov to create your own unique policies, providers, and suppression terms. Avoid the deployment of misconfigurations by integrating this process into the current workflows of developers. Facilitate automated annotations on pull or merge requests in your repositories, eliminating the need to establish a CI pipeline or perform routine checks. The Bridgecrew platform will automatically review new pull requests and provide comments highlighting any policy violations it uncovers, ensuring continuous compliance and security improvements in your cloud infrastructure. This proactive approach helps maintain best practices and enhances the overall security posture of your cloud environment.
Description
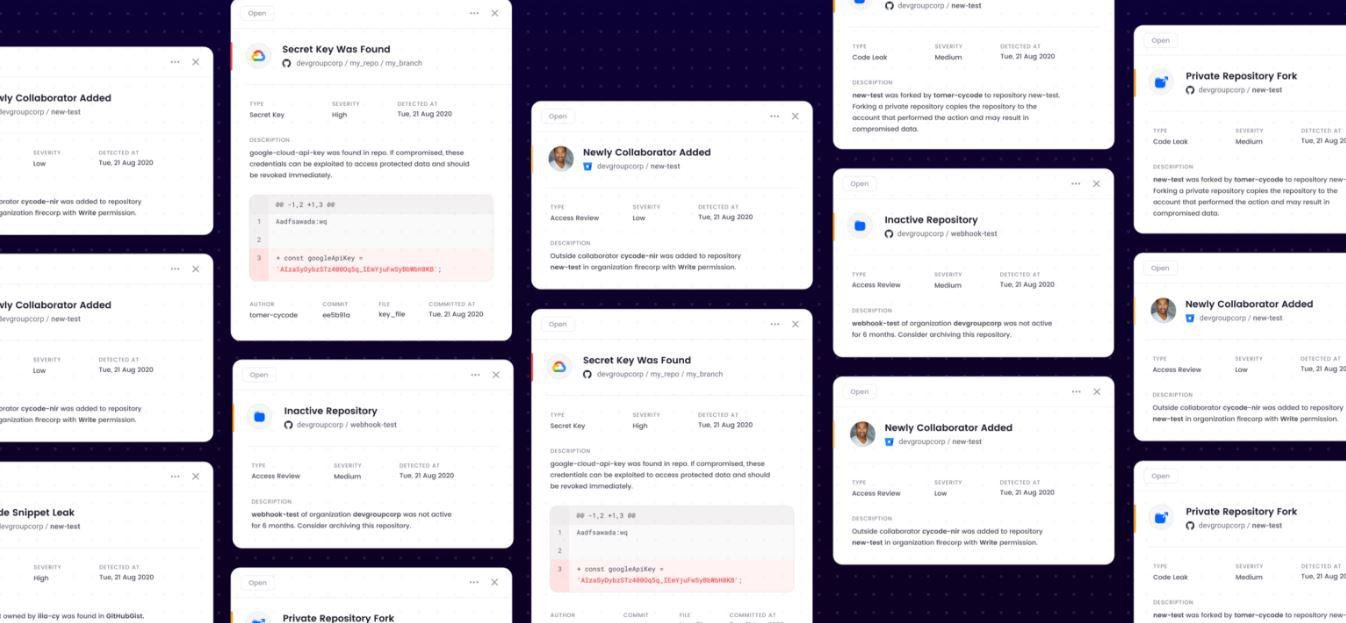
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
No
API Access
Has API
No



Integrations
Amazon Web Services (AWS)
Yes
GitHub
Yes
GitLab
Yes
Google Cloud Platform
Yes
Jenkins
Yes
Kubernetes
Yes
Microsoft Azure
Yes
Terraform
Yes
AWS CloudFormation
Yes
Brainboard
Yes
Integrations
Amazon Web Services (AWS)
Yes
GitHub
Yes
GitLab
Yes
Google Cloud Platform
Yes
Jenkins
Yes
Kubernetes
Yes
Microsoft Azure
Yes
Terraform
Yes
AWS CloudFormation
No
Brainboard
No
Pricing Details
Free
Open source
Free Trial
No
Free Version
Yes
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Prisma Cloud
Founded
2019
Country
United States
Website
www.checkov.io
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Static Code Analysis
Analytics / Reporting
No
Code Standardization / Validation
No
Multiple Programming Language Support
No
Provides Recommendations
No
Standard Security/Industry Libraries
No
Vulnerability Management
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
