Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
Astra PentestAstra's Pentest is a comprehensive solution for penetration testing. It includes an intelligent vulnerability scanner and in-depth manual pentesting. The automated scanner performs 10000+ security checks, including security checks for all CVEs listed in the OWASP top 10 and SANS 25. It also conducts all required tests to comply with ISO 27001 and HIPAA. Astra provides an interactive pentest dashboard which allows users to visualize vulnerability analysis, assign vulnerabilities to team members, collaborate with security experts, and to collaborate with security experts. The integrations with CI/CD platforms and Jira are also available if users don't wish to return to the dashboard each time they want to use it or assign a vulnerability for a team member.
-
Orca SecurityOrca Security is the pioneer of agentless cloud security that is trusted by hundreds of enterprises globally. Orca makes cloud security possible for enterprises moving to and scaling in the cloud with its patented SideScanning™ technology and Unified Data Model. The Orca Cloud Security Platform delivers the world's most comprehensive coverage and visibility of risks across AWS, Azure, Google Cloud and Kubernetes.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Criminal IP ASMCriminal IP's Attack Surface Management (ASM) is an intelligence-driven platform designed to continuously identify, catalog, and oversee all internet-connected assets linked to an organization, including overlooked and shadow resources, enabling teams to understand their actual external exposure from the perspective of potential attackers. This solution integrates automated asset detection with open-source intelligence (OSINT) methods, artificial intelligence enhancements, and sophisticated threat intelligence to reveal exposed hosts, domains, cloud services, IoT devices, and other internet-facing entry points, while also collecting evidence such as screenshots and metadata, and linking findings to known vulnerabilities and attacker techniques. By evaluating exposures through the lens of business relevance and risk, ASM emphasizes vulnerable elements and misconfigurations, providing instantaneous alerts and interactive dashboards that facilitate quicker investigations and remediation efforts. Furthermore, this comprehensive tool empowers organizations to proactively manage their security posture, ensuring that they remain vigilant against emerging threats.
-
ESET PROTECT AdvancedESET Protect Advanced offers a comprehensive cybersecurity solution for businesses of any size. It offers advanced endpoint security against ransomware and zero-day threats. It also includes full disk encryption to ensure legal compliance and data security. The solution uses adaptive scanning, cloud sandboxing and behavioral analysis for proactive cloud-based threats defense. Mobile threat protection secures Android and iOS with anti-malware and anti-theft. It also offers cloud app security, mail server protection, vulnerability and patch management, and cloud app protection. Multi-factor authentication and extended detection and reaction (XDR) improve threat detection and response. The solution provides a single pane of glass remote management to provide visibility into threats and users. It also offers advanced reporting and customized notifications.
-
HyperproofCompliance work eats engineering time. Hyperproof exists to give that time back by automating the parts of GRC that don't need a human: pulling evidence out of GitHub, Jira, ServiceNow, Snyk, and cloud storage on a schedule, running recurring tests against high-frequency controls, and kicking off a task automatically the moment something fails instead of waiting for the next audit cycle to find out. Under the hood, Hyperproof maps one control to 160+ frameworks (SOC 2, ISO 27001, HIPAA, NIST, and others), so a control tested once can satisfy several standards instead of forcing teams to rebuild the same work per framework. AI agents handle the first pass on evidence review and gap-flagging, leaving humans to make the actual judgment calls rather than hunting down documentation. Teams using it report cutting audit prep by roughly 350 hours a year, a 66% drop in duplicate controls, and about $150K saved annually on control orchestration. It also scales to messier org charts, with the ability to scope controls by business unit or entity instead of flattening everything into one program. Built in 2018 out of the Seattle area, Hyperproof is used by engineering and security-heavy orgs like Reddit, Fortinet, Appian, and Outreach that are tired of treating compliance as a manual, spreadsheet and email process and want it to run more like the rest of their infrastructure: automated, monitored, and auditable.
-
DriveStrikeDriveStrike is simple to use, implement, and manage. DriveStrike allows you to perform remote wipe, remote lock, or remote locate commands on any platform. Mobile device management MDM for mobile platforms. Integrated drive encryption support. Our support team is available to answer any questions, help you install our services, or manage your account. It's never been easier to protect your data and devices. We are happy to answer any questions you may have or help you understand how to best protect your data. Protect your business with a device- and data protection platform that keeps all devices protected with a single solution. Your Workstations, iPads and iPads, Smartphones as well as Tablets, Tablets, Tablets, and Laptops will be protected, organized, secure, & protected.
-
NeuBirdNeuBird is the Agentic Operations Center: one secure link to your telemetry and LLMs that resolves incidents, remembers every investigation, and shares one governed truth across your teams and agents.
-
ReflectizReflectiz is a web exposure management platform that enables organizations to proactively identify, monitor, and mitigate security, privacy, and compliance risks across their digital environments. It provides comprehensive visibility and control over first, third, and even fourth-party components like scripts, trackers, and open-source libraries—elements that are often missed by traditional security tools. The unique advantage of Reflectiz is that it operates remotely, without embedding code on customer websites. This ensures no impact on site performance, no access to sensitive user data, and no additional attack surface. By continuously monitoring all publicly available components, Reflectiz identifies hidden risks in your digital supply chain, helping to detect vulnerabilities and compliance issues in real-time. With a centralized dashboard, Reflectiz gives businesses a holistic view of their web assets, making it easier to manage risk across all digital properties. The platform allows teams to establish baselines for approved behaviors, swiftly identifying deviations that may indicate threats. Reflectiz is particularly valuable for industries such as eCommerce, healthcare, and finance, where managing third-party risks is crucial. It helps businesses enhance security, reduce attack surfaces, and maintain compliance without requiring any changes to website code, offering continuous monitoring and detailed insights into external component behaviors.
Description
Boman.ai seamlessly integrates into your CI/CD pipeline with just a few commands and requires minimal setup, eliminating the need for extensive planning or specialized knowledge. This solution combines SAST, DAST, SCA, and secret scanning into a single, cohesive integration that supports various programming languages. By leveraging open-source scanners, Boman.ai significantly reduces your application security costs, sparing you from the need to invest in costly security tools. Its AI/ML capabilities enhance the accuracy of results by eliminating false positives and providing correlation for effective prioritization and remediation. The SaaS platform features a comprehensive dashboard that consolidates all scan results in one accessible location, allowing for easy correlation and insightful analysis to enhance your application security posture. Users can efficiently manage the vulnerabilities identified by the scanner, enabling prioritization, triage, and effective remediation of security issues. With Boman.ai, you can streamline your security processes and gain a clearer understanding of your application's vulnerabilities.
Description
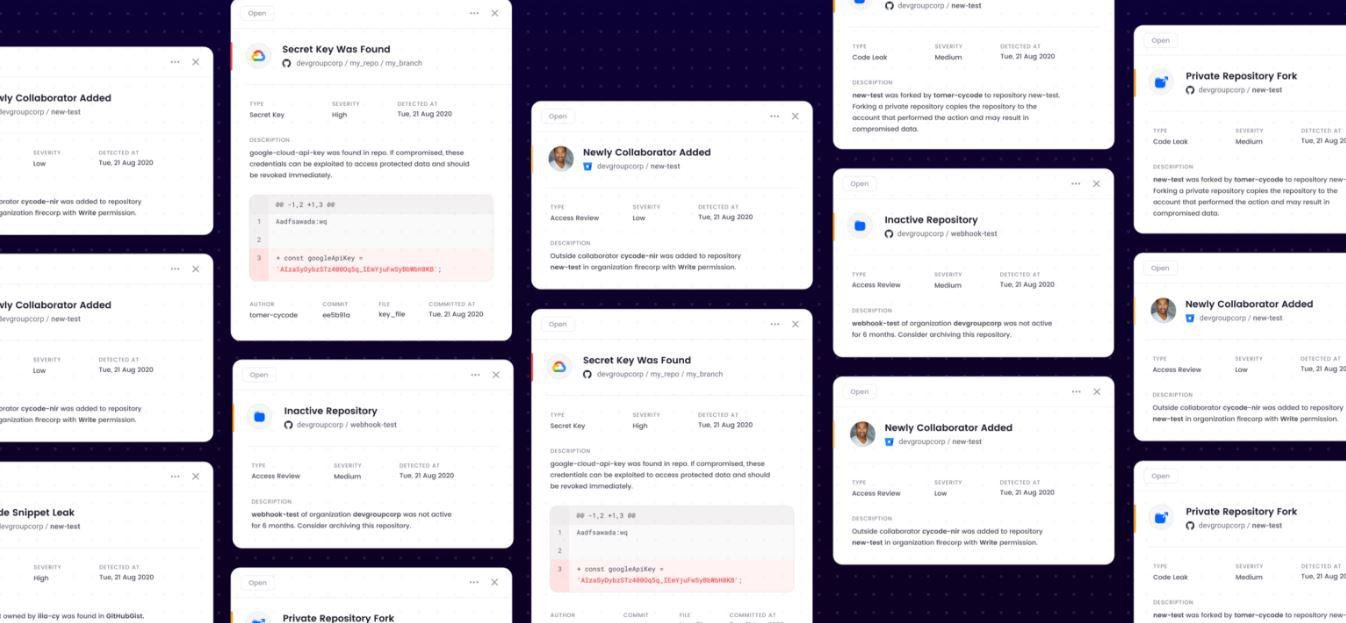
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
No
API Access
Has API
No



Integrations
CircleCI
Yes
GitHub
Yes
GitLab
Yes
Jenkins
Yes
Travis CI
Yes
Amazon Web Services (AWS)
No
Axonius
No
Azure DevOps Server
Yes
Cobalt
No
Databricks
No
Integrations
CircleCI
Yes
GitHub
Yes
GitLab
Yes
Jenkins
Yes
Travis CI
Yes
Amazon Web Services (AWS)
Yes
Axonius
Yes
Azure DevOps Server
No
Cobalt
Yes
Databricks
Yes
Pricing Details
No price information available.
Free Trial
No
Free Version
Yes
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Boman.ai
Country
India
Website
boman.ai/
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Vulnerability Management
Asset Discovery
No
Asset Tagging
No
Network Scanning
No
Patch Management
No
Policy Management
No
Prioritization
No
Risk Management
No
Vulnerability Assessment
No
Web Scanning
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
