Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
Source DefenseSource Defense is an essential element of web safety that protects data at the point where it is entered. Source Defense Platform is a simple, yet effective solution to data security and privacy compliance. It addresses threats and risks that arise from the increased use JavaScript, third party vendors, and open source code in your web properties. The Platform offers options for securing code as well as addressing an ubiquitous gap in managing third-party digital supply chains risk - controlling actions of third-party, forth-party and nth-party JavaScript that powers your website experience. Source Defense Platform provides protection against all types of client-side security incidents, including keylogging, formjacking and digital skimming. Magecart is also protected. - by extending the web security beyond the browser to the server.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
Altium DevelopAltium Develop is a collaborative platform for modern electronics engineering teams that connects requirements management, PCB design, systems engineering, and manufacturing workflows. Built on Altium Designer and Altium 365, the platform provides a centralized environment for design collaboration, requirements traceability, BOM management, supply chain visibility, and engineering change management. Altium Develop helps hardware organizations maintain alignment between requirements, design decisions, and manufacturing outcomes while supporting distributed engineering teams through cloud-based collaboration. Core Features: • PCB design collaboration • ECAD-MCAD co-design workflows • Component and supply chain visibility • BOM and engineering change management • Design review and approval workflows • Cloud-native team collaboration • Requirements management and traceability Used by electronics teams building complex PCB-based products, Altium Develop is frequently evaluated alongside Cadence OrCAD, Cadence Allegro, Autodesk Fusion Electronics, KiCad, Siemens Xpedition, and SOLIDWORKS PCB for organizations seeking greater collaboration and lifecycle visibility across hardware development programs.
-
SafeticaSafetica Intelligent Data Security protects sensitive enterprise data wherever your team uses it. Safetica is a global software company that provides Data Loss Prevention and Insider Risk Management solutions to organizations. ✔️ Know what to protect: Accurately pinpoint personally identifiable information, intellectual property, financial data, and more, wherever it is utilized across the enterprise, cloud, and endpoint devices. ✔️ Prevent threats: Identify and address risky activities through automatic detection of unusual file access, email interactions, and web activity. Receive the alerts necessary to proactively identify risks and prevent data breaches. ✔️ Secure your data: Block unauthorized exposure of sensitive personal data, trade secrets, and intellectual property. ✔️ Work smarter: Assist teams with real-time data handling cues as they access and share sensitive information.
-
Bitdefender Ultimate Small Business SecurityBitdefender Small Business Security provides robust, enterprise-level cyber-defense tailored for smaller companies, ensuring protection across various platforms including Windows, macOS, iOS, and Android. With a centralized management system that is user-friendly, it allows organizations lacking dedicated IT personnel to efficiently implement and oversee their security measures from a single interface. The solution features a multi-layered approach to endpoint protection, incorporating machine learning, behavioral analysis, real-time monitoring, process termination, and rollback capabilities to safeguard against both known and emerging threats. Additionally, it includes ransomware prevention and remediation strategies that detect unusual encryption activities and facilitate file recovery from backups. Users are also protected against fileless attacks, with measures like memory and back-injection interference as well as script blocking. The software further enhances security by preventing phishing and fraud through the blocking of malicious websites and alerting users accordingly, while offering advanced exploit protection with real-time shields for common applications such as browsers, Office software, and Adobe Reader, thus ensuring all-encompassing endpoint security. This comprehensive suite of features makes it an ideal choice for small businesses seeking to fortify their cybersecurity defenses.
-
Jesta Vision SuiteJesta I.S. has been in business for over 50 years. Jesta I.S. is a global provider of enterprise software solutions to retailers, etailers, wholesalers and brand manufacturers, specializing in apparel and footwear. The Vision Suite is a cloud-based, organically engineered platform that optimizes back/front-end supply chain operations. This includes everything from trade/product/demand management to merchandising and POS. It eliminates inefficiencies caused by disjointed apps and provides real-time visibility into enterprise inventory, cross-channel orders and AI-driven CRM data. It supports multiple brands, currencies, languages, and helps businesses create seamless omnichannel shopping experiences.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
Keeper SecurityPassword security is the foundation of cybersecurity. Keeper's powerful password security platform will protect your business from cyberthreats and data breaches related to passwords. Research shows that 81% of data breaches can be attributed to weak passwords. Password security platforms are an affordable and easy way for companies to address the root cause of most data breaches. Your business can significantly reduce the risk of data breaches by implementing Keeper. Keeper creates strong passwords for all websites and apps, then secures them on all devices. Each employee receives a private vault to store and manage their passwords, credentials and files, as well as private client data. Employees will save time and frustration by not having to remember, reset, reuse, or remember passwords. Industry compliance is achieved through strict and customizable role-based access controls. This includes 2FA, usage auditing, and event reporting.
-
ChainstackChainstack's APIs and software are used by thousands of businesses, large and small, to build, scale, and maintain blockchain applications. To ensure your security and control, Chainstack's APIs offer secure node connections and key security best practices. Invite other members to join your network and deploy their infrastructure using simple network management tools. You can build and deploy the blockchain protocol that suits your needs. The protocol will never be updated or modified again. Chainstack's managed services for blockchain make it easy to launch, join, and scale decentralized networks. You can now safely experiment with enterprise-grade tools and services and then run production. Continuously monitor and provision your resources.
Description
Streamline your software supply chain security processes with automation, allowing for the proactive identification and management of anomalies and risks within your development environment, ensuring that developers can confidently trust their code commits. Implement automated developer access management through behavior-driven systems with self-service options available via platforms like Slack or Teams. Maintain continuous oversight of developer actions to quickly identify and address any unusual behavior. Detect and eliminate hardcoded secrets before they can affect production environments. Enhance your security posture by gaining comprehensive visibility into open-source licenses, infrastructure vulnerabilities, and OpenSSF scorecards across your organization in just a few minutes. Arnica stands out as a behavior-focused software supply chain security solution tailored for DevOps, delivering proactive protection by streamlining daily security operations while empowering developers to take charge of security without increasing risk or hindering their pace of work. Furthermore, Arnica provides the tools necessary to facilitate ongoing advancements towards the principle of least privilege for developer permissions, ensuring a more secure development process overall. With Arnica, your team can maintain high productivity levels while safeguarding the integrity of your software supply chain.
Description
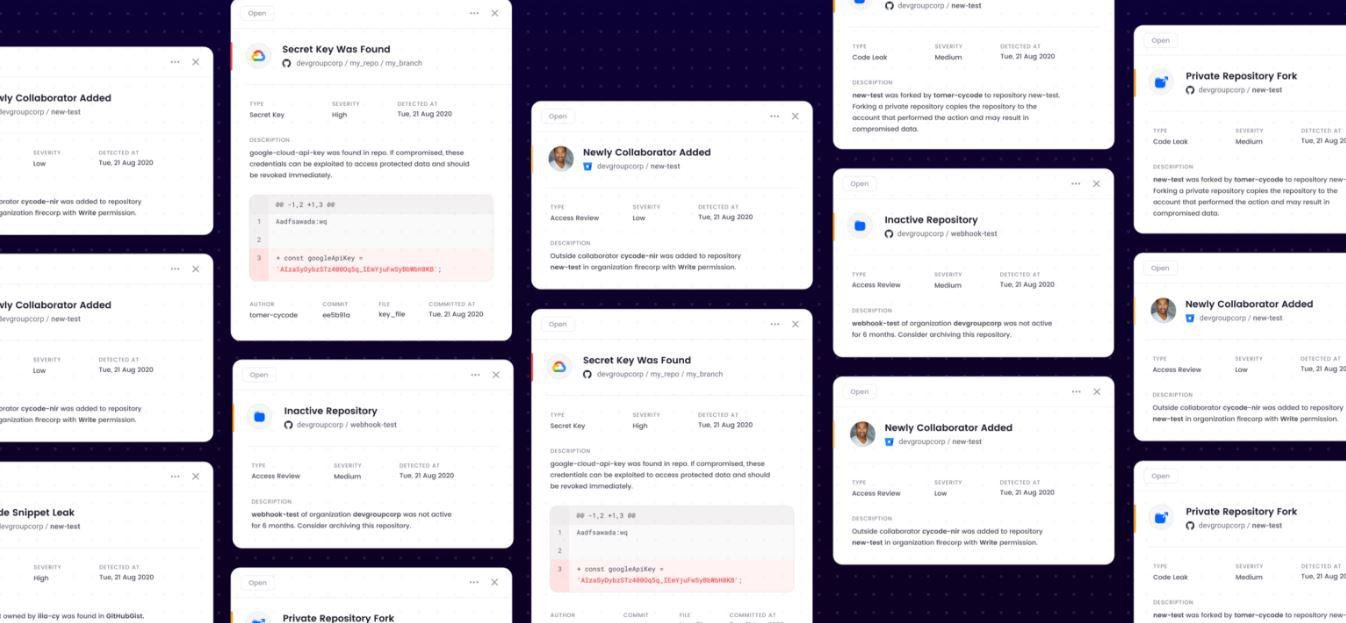
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
No
API Access
Has API
No



Integrations
GitHub
Yes
Slack
Yes
Amazon Web Services (AWS)
No
Axonius
No
Azure DevOps
Yes
Cobalt
No
CycloneDX
Yes
Databricks
No
Flexport
No
GitLab
No
Integrations
GitHub
Yes
Slack
Yes
Amazon Web Services (AWS)
Yes
Axonius
Yes
Azure DevOps
No
Cobalt
Yes
CycloneDX
No
Databricks
Yes
Flexport
Yes
GitLab
Yes
Pricing Details
Free
Free Trial
Yes
Free Version
Yes
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
Yes
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Arnica
Founded
2022
Country
United States
Website
www.arnica.io
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
