Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
Jama ConnectJama Connect®, a product development platform, uniquely creates Living Requirements™. This digital thread is created through siloed, test, and risk activities to provide end to end compliance, risk mitigation, process improvement, and compliance. Companies creating complex products, systems, and software can now define, align, and execute on what they need. This reduces the time and effort required to prove compliance and saves on rework. You can be sure of success by choosing a solution that is easy-to-use, flexible, and offers support and services that are adoption-oriented.
-
Planview Software Product DeliveryPlanview Software Product Delivery Solution is a comprehensive enterprise platform that provides delivery intelligence by connecting strategy to execution across development toolchains. It integrates seamlessly with tools such as Azure DevOps, GitHub, and Jira to collect and unify real-time data from across teams. This allows organizations to gain full visibility into their delivery processes and make informed decisions. The platform includes features like cross-team dependency management, capacity planning, and agile planning at both team and portfolio levels. It enables users to analyze workflows, identify bottlenecks, and optimize delivery performance. Advanced analytics, including DORA metrics, provide insights into engineering efficiency and outcomes. AI-powered roadmapping helps align business objectives with execution strategies. The solution also supports connected OKRs to ensure teams stay aligned with organizational goals. Portfolio-level investment planning and scenario modeling allow leaders to evaluate different strategies. Risk signals are surfaced early through configurable thresholds and flow metrics. By replacing manual reporting with real-time dashboards, Planview improves transparency and decision-making. Ultimately, it helps enterprises deliver digital products more efficiently and with measurable impact.
-
Rocket z/Assure VAPYour mission-critical systems carry the weight of your entire organization. Protecting them shouldn't leave you guessing about hidden vulnerabilities or compliance risks. Rocket® z/Assure™ Vulnerability Analysis Program (VAP) is a specialized mainframe security solution built to proactively scan and safeguard your most valuable environments. By identifying system-level risks before they become active threats, we partner with you to ensure your infrastructure remains locked down, resilient, and fully compliant. We understand the responsibility of managing enterprise security, and our tool gives you the exact insights you need to confidently eliminate weak points. Key benefits for your security team: - Identify and resolve hidden vulnerabilities with deep, automated scanning. - Protect your mission-critical data from evolving external and internal threats. - Streamline compliance reporting with clear, actionable security insights. Take control of your mainframe security. Partner with Rocket Software to protect your digital foundation today.
-
PowerDMARCPowerDMARC is a robust email security solution that safeguards your brand reputation and email communications from threats like spoofing, phishing, and ransomware. By leveraging advanced technologies such as DMARC, SPF, DKIM, BIMI, MTA-STS, and TLS-RPT, PowerDMARC empowers you to protect your email infrastructure. With a user-friendly platform, PowerDMARC simplifies complex configurations, enabling you to easily manage and monitor your email security posture. AI-powered threat intelligence provides valuable insights to proactively identify and mitigate emerging threats. Trusted by over 2000 organizations globally, including Fortune 100 companies and governments, PowerDMARC is your trusted partner in securing your email infrastructure.
-
Gemini Enterprise Agent PlatformGemini Enterprise Agent Platform is Google Cloud’s next-generation system for designing and managing advanced AI agents across the enterprise. Built as the successor to Vertex AI, it unifies model selection, development, and deployment into a single scalable environment. The platform supports a vast ecosystem of over 200 AI models, including Google’s latest Gemini innovations and popular third-party models. It offers flexible development tools like Agent Studio for visual workflows and the Agent Development Kit for deeper customization. Businesses can deploy agents that operate continuously, maintain long-term memory, and handle multi-step processes with high efficiency. Security and governance are central, with features such as agent identity verification, centralized registries, and controlled access through gateways. The platform also enables seamless integration with enterprise systems, allowing agents to interact with data, applications, and workflows securely. Advanced monitoring tools provide real-time insights into agent behavior and performance. Optimization features help refine agent logic and improve accuracy over time. By combining automation, intelligence, and governance, the platform helps organizations transition to autonomous, AI-driven operations. It ultimately supports faster innovation while maintaining enterprise-grade reliability and control.
-
ParasoftParasoft's mission is to provide automated testing solutions and expertise that empower organizations to expedite delivery of safe and reliable software. A powerful unified C and C++ test automation solution for static analysis, unit testing and structural code coverage, Parasoft C/C++test helps satisfy compliance with industry functional safety and security requirements for embedded software systems.
-
Interfacing Integrated Management System (IMS)Interfacing’s Integrated Management System (IMS ) is an AI-supported platform that brings BPM, QMS, Document Control, and GRC together in one environment. Teams use IMS to design and manage processes, govern documentation, oversee risks, and demonstrate compliance with complete visibility and reliable audit evidence. Built for sectors that depend on strict oversight, such as aerospace, life sciences, public sector, and financial services, IMS offers real-time monitoring, automated workflows, and AI-driven analytics that strengthen quality and lower operational exposure. The system is ISO 27001 certified and validated for 21 CFR Part 11, ensuring secure and compliant use in regulated operations. IMS also provides low-code automation, process mining, audit tools, training management, CAPA workflows, and dashboards that help organizations improve performance and maintain regulatory control. AI enhances governance, improves precision, and supports continuous compliance.
-
GearsetGearset is a full‑featured Salesforce DevOps solution built for the enterprise, giving teams the tools to adopt best practices across every stage of the DevOps lifecycle. From metadata and CPQ deployments to CI/CD, testing, code analysis, sandbox seeding, backups, archiving, and observability, Gearset gives teams unmatched insight and control over their Salesforce workflows. Over 3,000 organizations — including names like McKesson and IBM — rely on Gearset to deliver with security and scale in mind. With advanced governance, detailed audit trails, SOX/ISO/HIPAA support, multi‑team pipelines, integrated security checks, and adherence to ISO 27001, SOC 2, GDPR, CCPA/CPRA, and HIPAA, Gearset combines enterprise‑ready compliance with rapid onboarding and an intuitive interface — all in one platform. Leading firms in finance, healthcare, and tech trust Gearset to power their DevOps initiatives without adding complexity.
-
D&B Risk AnalyticsGlobally, teams in risk, procurement, and compliance are under pressure to manage geopolitical risks and business risks. Third-party risks are impacted by the complexity of domestic and international businesses, as well as complex and diverse regulations. It is crucial that companies proactively manage third-party relationships. This cutting-edge platform, powered by D&B Data Cloud's 520M+ Global Business Records with 2B+ annual updates for third-party risks, is an AI-powered solution that mitigates and monitors counterparty risk on a continual basis. D&B Risk Analytics uses best-in class risk data, including alerts for high-risk purchases and match points of more than a billion. This helps to drive informed decisions. Intelligent workflows allow for quick and thorough screening. Receive alerts on key business indicators.
Description
Archipelo serves as a comprehensive platform for managing developer security posture, assisting organizations in protecting their software development lifecycle (SDLC) by delivering instantaneous insights on developer activities, the utilization of AI coding tools, and governance of those tools. Among its key features is Developer Detection Response (DevDR), which enables proactive identification and reduction of security vulnerabilities, alongside Automated Tool Governance designed to curb shadow IT occurrences. Additionally, the AI Code Usage & Risk Monitor helps maintain secure coding standards by tracking software development activities. By effortlessly integrating into CI/CD pipelines, Archipelo not only captures developer actions but also produces actionable insights that bolster security measures, reduce risks, and ensure adherence to compliance throughout the software development journey. This makes Archipelo an essential element for organizations aiming to enhance their security framework in a rapidly evolving technological landscape.
Description
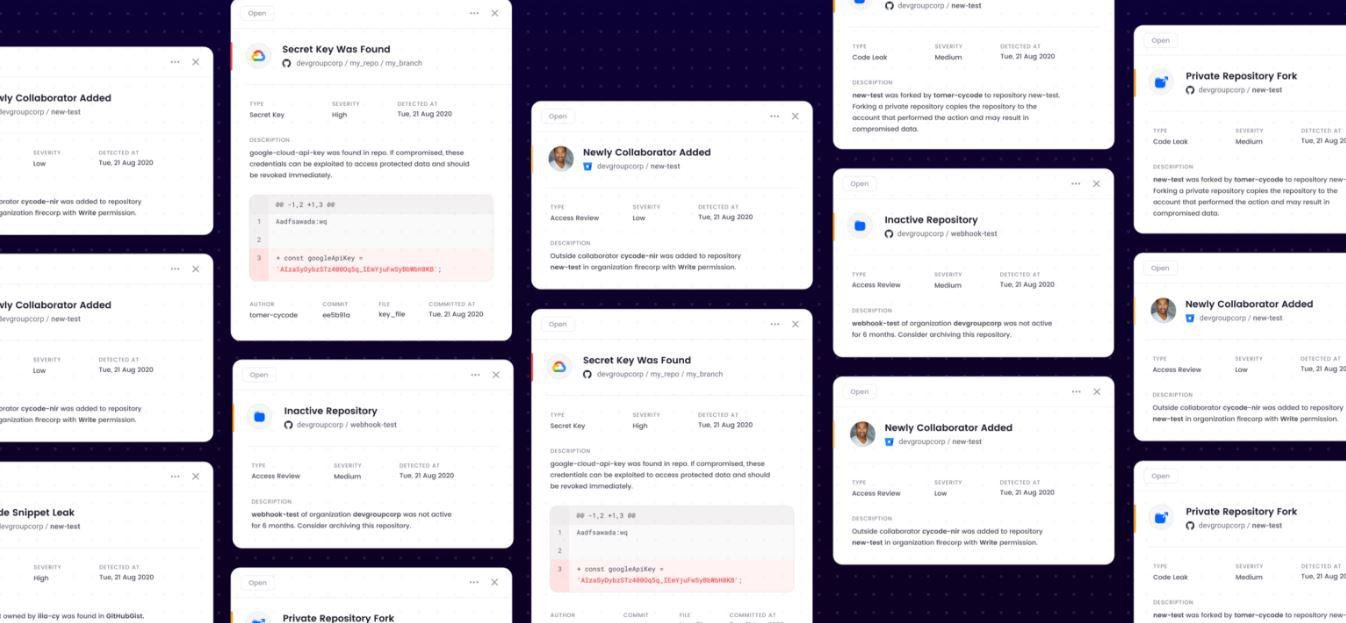
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
No
API Access
Has API
No



Integrations
GitHub
Yes
GitLab
Yes
Jira
Yes
Slack
Yes
Amazon Web Services (AWS)
No
Axonius
No
Checkov
Yes
Cobalt
No
Databricks
No
Dependabot
Yes
Integrations
GitHub
Yes
GitLab
Yes
Jira
Yes
Slack
Yes
Amazon Web Services (AWS)
Yes
Axonius
Yes
Checkov
No
Cobalt
Yes
Databricks
Yes
Dependabot
No
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
Yes
Webinars
No
Live Training (Online)
No
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Archipelo
Founded
2020
Country
United States
Website
archipelo.com
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
