Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
Airlock DigitalAirlock Digital delivers an easy-to-manage and scalable application control solution to protect endpoints with confidence. Built by cybersecurity professionals and trusted by organizations worldwide, Airlock Digital enforces a Deny by Default security posture to block all untrusted code, including unknown applications, unwanted scripts, malware, and ransomware.
-
Securden Password Vault for EnterprisesSecurden Password Vault is an enterprise-grade password management solution that allows you to securely store, organize, share, manage, and keep track of all human and machine identities. With a sleek access management system, Securden lets your IT teams share administrator credentials and effectively automate the management of privileged accounts in your organization. Securden seamlessly integrates with industry solutions like SIEM, SAML-based SSO, AD, and Azure AD among others to provide a smooth deployment in any organization. With Securden, organizations can rest easy as all their sensitive data is protected with strong encryption methods and supported by a robust high availability setup. Securden offers drilled-down granular access controls that allow users to grant access to accounts without revealing the underlying credentials in a just-in-time fashion. Securden Password Vault can be deployed both on-premise for self-hosting and on the cloud (SaaS).
-
ManageEngine ADAudit PlusADAudit Plus enhances the security and compliance of your Windows Server environment by delivering comprehensive insights into all operational activities. It offers a detailed overview of modifications made to Active Directory (AD) resources, encompassing AD objects and their respective attributes, group policies, and more. By conducting thorough AD audits, organizations can identify and mitigate insider threats, misuse of privileges, and other signs of potential security breaches, thereby bolstering their overall security framework. The tool enables users to monitor intricate details within AD, including entities such as users, computers, groups, organizational units (OUs), group policy objects (GPOs), schemas, and sites, along with their associated attributes. Furthermore, it tracks user management activities like the creation, deletion, password resets, and alterations in permissions, providing insights into the actions taken, the responsible individuals, the timing, and the originating locations. Additionally, it allows organizations to monitor the addition or removal of users from security and distribution groups, ensuring that access privileges are kept to the necessary minimum, which is critical for maintaining a secure environment. This level of oversight is vital for proactive security management and compliance adherence.
-
PowerDMARCPowerDMARC is a robust email security solution that safeguards your brand reputation and email communications from threats like spoofing, phishing, and ransomware. By leveraging advanced technologies such as DMARC, SPF, DKIM, BIMI, MTA-STS, and TLS-RPT, PowerDMARC empowers you to protect your email infrastructure. With a user-friendly platform, PowerDMARC simplifies complex configurations, enabling you to easily manage and monitor your email security posture. AI-powered threat intelligence provides valuable insights to proactively identify and mitigate emerging threats. Trusted by over 2000 organizations globally, including Fortune 100 companies and governments, PowerDMARC is your trusted partner in securing your email infrastructure.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
KitecyberKitecyber: Data & Gen AI Security, Built on the Endpoint Your most sensitive data leaves through browsers, Gen AI prompts, SaaS uploads, and clipboards — faster than any network tool can catch it. Kitecyber stops that at the source, with a single lightweight agent that runs directly on the endpoint and acts the instant data is touched, not after it's already gone. Because it lives on the device, Kitecyber has full context — device, OS, process, data, user, and network activity together, in real time. That's the vantage point network- and cloud-only tools simply don't have. Data security that keeps up with your data. Kitecyber classifies sensitive information with LLM-powered, context-aware intelligence across 80+ categories — PII, PHI, PCI, source code, IP — at over 90% accuracy, not brittle keyword matching. It tracks data lineage through screenshots, encoding, and file conversion that defeat traditional scanners, and blocks policy violations inline, before data ever leaves the endpoint. Gen AI security for the age of AI agents. Kitecyber tracks sensitive data pasted or uploaded into tools like ChatGPT, Claude, and Gemini and stops it in real time. It discovers shadow AI reaching your devices and extends visibility to the AI agents now acting on your users' behalf — the blind spot identity- and network-based tools were never built to see. Trusted and proven. Kitecyber secures fast-growing fintech, BFSI, and SMB organizations in highly regulated environments, partnering with GRC leaders like Scrut Automation to unify security and compliance. It's SOC 2 Type II compliant, deploys in about a day, and delivers enterprise-grade protection without enterprise complexity. See what full-context data and Gen AI security looks like. Learn more at kitecyber.com.
-
Nexcess Managed CloudNexcess is a managed cloud hosting solution designed to streamline infrastructure while providing exceptional performance, security, and scalability for essential business applications. This platform integrates cloud hosting, networking, compliance, application management, and automation into a cohesive environment, thereby eliminating the necessity of coordinating multiple vendors or tools. It effectively reduces operational complexities, allowing expert teams to manage orchestration, security, system uptime, and maintenance, which empowers users to concentrate on developing and expanding their applications. With dedicated computing resources, Nexcess guarantees consistent performance and cost predictability, complemented by fixed-cost billing that alleviates the uncertainties typically linked to public cloud services. Furthermore, it incorporates comprehensive governance and compliance functionalities that adhere to standards like HIPAA and PCI-DSS, alongside ongoing security monitoring, firewalls, and DDoS mitigation. Ultimately, Nexcess not only enhances operational efficiency but also ensures that businesses can scale securely and confidently in a rapidly evolving digital landscape.
-
SafeticaSafetica Intelligent Data Security protects sensitive enterprise data wherever your team uses it. Safetica is a global software company that provides Data Loss Prevention and Insider Risk Management solutions to organizations. ✔️ Know what to protect: Accurately pinpoint personally identifiable information, intellectual property, financial data, and more, wherever it is utilized across the enterprise, cloud, and endpoint devices. ✔️ Prevent threats: Identify and address risky activities through automatic detection of unusual file access, email interactions, and web activity. Receive the alerts necessary to proactively identify risks and prevent data breaches. ✔️ Secure your data: Block unauthorized exposure of sensitive personal data, trade secrets, and intellectual property. ✔️ Work smarter: Assist teams with real-time data handling cues as they access and share sensitive information.
Description
To effectively secure and oversee the utilization of vital SaaS applications, it is essential for Security, Compliance, and IT teams to have a robust solution offering immediate insights, proactive monitoring of security posture, standardized event streams, and efficient compliance tools. AppOmni stands out as the sole SaaS Security Posture Management solution that equips teams with all necessary resources for success, covering areas from posture management and monitoring to detection and ongoing compliance. The platform allows for instant identification of misconfigurations that could compromise the security integrity of essential SaaS applications. It also provides comprehensive visibility into your SaaS environments, streamlining data to integrate seamlessly with your existing security tools. Forget about spreadsheets and manual access reviews; with AppOmni, you can confidently ensure your compliance requirements are met. Each SaaS application presents a unique landscape with hundreds of settings, thousands of API calls, and a tailored data access model. By leveraging AppOmni, organizations can navigate the complexities of SaaS security with ease and assurance.
Description
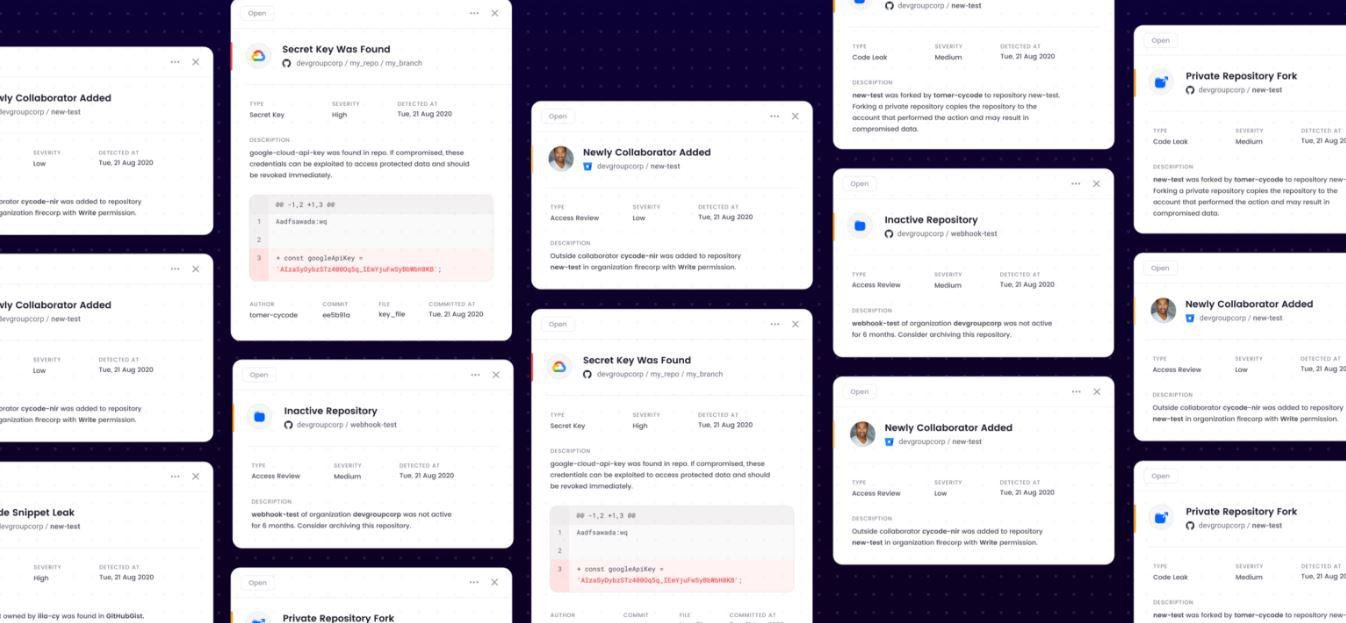
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
No
API Access
Has API
No



Integrations
Amazon Web Services (AWS)
No
Axonius
No
CircleCI
No
Cobalt
No
Flexport
No
GitHub
No
GitLab
No
Google Cloud Platform
No
Grubhub
No
Jenkins
No
Integrations
Amazon Web Services (AWS)
Yes
Axonius
Yes
CircleCI
Yes
Cobalt
Yes
Flexport
Yes
GitHub
Yes
GitLab
Yes
Google Cloud Platform
Yes
Grubhub
Yes
Jenkins
Yes
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
No
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
No
Webinars
No
Live Training (Online)
No
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
AppOmni
Founded
2018
Country
United States
Website
appomni.com
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
IT Security
Anti Spam
No
Anti Virus
No
Email Attachment Protection
No
Event Tracking
No
IP Protection
No
Internet Usage Monitoring
No
Intrusion Detection System
No
Spyware Removal
No
Two-Factor Authentication
No
Vulnerability Scanning
No
Web Threat Management
No
Web Traffic Reporting
No
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
