Average Ratings 0 Ratings
Average Ratings 0 Ratings
Similar Products
-
Aikido SecurityAikido is the all-in-one security platform for development teams to secure their complete stack, from code to cloud. Aikido centralizes all code and cloud security scanners in one place. Aikido offers a range of powerful scanners including static code analysis (SAST), dynamic application security testing (DAST), container image scanning, and infrastructure-as-code (IaC) scanning. Aikido integrates AI-powered auto-fixing features, reducing manual work by automatically generating pull requests to resolve vulnerabilities and security issues. It also provides customizable alerts, real-time vulnerability monitoring, and runtime protection, enabling teams to secure their applications and infrastructure seamlessly.
-
CloudflareCloudflare is the foundation of your infrastructure, applications, teams, and software. Cloudflare protects and ensures the reliability and security of your external-facing resources like websites, APIs, applications, and other web services. It protects your internal resources, such as behind-the firewall applications, teams, devices, and devices. It is also your platform to develop globally scalable applications. Your website, APIs, applications, and other channels are key to doing business with customers and suppliers. It is essential that these resources are reliable, secure, and performant as the world shifts online. Cloudflare for Infrastructure provides a complete solution that enables this for everything connected to the Internet. Your internal teams can rely on behind-the-firewall apps and devices to support their work. Remote work is increasing rapidly and is putting a strain on many organizations' VPNs and other hardware solutions.
-
ReflectizReflectiz is a web exposure management platform that enables organizations to proactively identify, monitor, and mitigate security, privacy, and compliance risks across their digital environments. It provides comprehensive visibility and control over first, third, and even fourth-party components like scripts, trackers, and open-source libraries—elements that are often missed by traditional security tools. The unique advantage of Reflectiz is that it operates remotely, without embedding code on customer websites. This ensures no impact on site performance, no access to sensitive user data, and no additional attack surface. By continuously monitoring all publicly available components, Reflectiz identifies hidden risks in your digital supply chain, helping to detect vulnerabilities and compliance issues in real-time. With a centralized dashboard, Reflectiz gives businesses a holistic view of their web assets, making it easier to manage risk across all digital properties. The platform allows teams to establish baselines for approved behaviors, swiftly identifying deviations that may indicate threats. Reflectiz is particularly valuable for industries such as eCommerce, healthcare, and finance, where managing third-party risks is crucial. It helps businesses enhance security, reduce attack surfaces, and maintain compliance without requiring any changes to website code, offering continuous monitoring and detailed insights into external component behaviors.
-
Orca SecurityOrca Security is the pioneer of agentless cloud security that is trusted by hundreds of enterprises globally. Orca makes cloud security possible for enterprises moving to and scaling in the cloud with its patented SideScanning™ technology and Unified Data Model. The Orca Cloud Security Platform delivers the world's most comprehensive coverage and visibility of risks across AWS, Azure, Google Cloud and Kubernetes.
-
GraylogGraylog is the AI-powered SIEM and log management platform built to help security and IT operations teams work faster, stay focused, and stay in control. It brings together all your event data in one place so teams can detect real threats quickly, investigate efficiently, and manage data costs predictably—without compromise. Graylog’s explainable AI turns noise into clarity, highlighting what matters most and guiding analysts through consistent, confident response steps. Its open, flexible architecture adapts to any environment, empowering organizations to scale and evolve without being locked into rigid systems or unpredictable pricing. With Graylog Security, Enterprise, API Security, and Open, more than 60,000 organizations worldwide rely on Graylog to deliver faster insight, simpler operations, and a smarter path to SIEM without compromise.
-
FerootFeroot Security is a global leader in AI-powered website and web application compliance and security. Feroot AI protects digital experiences from hidden threats while continuously enforcing compliance with PCI DSS 4.0.1, HIPAA rules on online tracking technologies, CCPA/CPRA, GDPR, CIPA, and over 50 global laws and standards. The Feroot AI Platform replaces manual compliance work and operational overhead with continuous automation. What once required months of effort across security, engineering, and legal teams can now be deployed in minutes, delivering real-time protection and audit-ready evidence. Feroot unifies critical capabilities into a single platform, including JavaScript behavior analysis, web compliance scanning, third-party script monitoring, consent enforcement, and data privacy posture management. It is purpose-built to detect and stop web-based threats such as Magecart, formjacking, e-skimming, and unauthorized tracking on high-risk assets like payment pages, login flows, iframes, and healthcare portals. Trusted by Fortune 500 enterprises, healthcare providers, retailers, SaaS platforms, utilities, payment service providers, universities, and public sector organizations, Feroot safeguards hundreds of millions of users worldwide. Feroot AI solutions include PaymentGuard AI, HealthData Shield AI, AlphaPrivacy AI, CodeGuard AI, and MobileGuard AI. Visit feroot for more information.
-
JscramblerJscrambler is the leader in Client-Side Security, protecting the code, data, and digital interactions that power today’s modern web applications. Modern applications are changing rapidly as development teams adopt AI-generated code, rely on third-party software components, and embed AI-powered agents into digital experiences. Meanwhile, sensitive information is increasingly created and processed in the browser itself. This creates a critical gap in enterprise security: organizations need to govern not only what code enters an application, but how that code, scripts, and data behave when the application runs. Jscrambler closes that gap with a Client-Side Security Platform built around its Behavioral Enforcement Core. The platform continuously monitors and enforces how application code, including AI-generated code, third-party scripts, AI agents, and sensitive data behave in the browser. By enforcing software integrity and data governance at runtime, Jscrambler gives organizations control at the point where code executes and data is created—before sensitive information can be exposed or transmitted. Organizations across retail, financial services, travel, healthcare, and other industries use Jscrambler to detect and stop client-side attacks, protect against risks introduced by AI-developed and third-party code, control AI-driven data flows, and strengthen compliance with requirements including PCI DSS, GDPR, HIPAA, CIPA, CCPA, and the EU AI Act.
-
KrakenDEngineered for peak performance and efficient resource use, KrakenD can manage a staggering 70k requests per second on just one instance. Its stateless build ensures hassle-free scalability, sidelining complications like database upkeep or node synchronization. In terms of features, KrakenD is a jack-of-all-trades. It accommodates multiple protocols and API standards, offering granular access control, data shaping, and caching capabilities. A standout feature is its Backend For Frontend pattern, which consolidates various API calls into a single response, simplifying client interactions. On the security front, KrakenD is OWASP-compliant and data-agnostic, streamlining regulatory adherence. Operational ease comes via its declarative setup and robust third-party tool integration. With its open-source community edition and transparent pricing model, KrakenD is the go-to API Gateway for organizations that refuse to compromise on performance or scalability.
-
HSI DonesafeHSI Donesafe redefines EHS management with a no-code, cloud-based platform that transforms complex processes into streamlined, user-friendly workflows. Trusted across industries, Donesafe consolidates tracking, management, and reporting into one accessible platform, making compliance simpler and safety more effective. Donesafe’s adaptable design allows teams to customize workflows, forms, and dashboards to meet evolving compliance needs. With tools for incident reporting, audits, training, and risk assessment, staying ahead of regulatory changes has never been easier. Key Features: - Customizable workflows to align with regulations - Real-time insights for live safety tracking - Scalable design that grows with your team - Streamlined compliance tools for smooth audits and reporting Empower your EHS team to achieve safety excellence with HSI Donesafe.
-
D&B Risk AnalyticsGlobally, teams in risk, procurement, and compliance are under pressure to manage geopolitical risks and business risks. Third-party risks are impacted by the complexity of domestic and international businesses, as well as complex and diverse regulations. It is crucial that companies proactively manage third-party relationships. This cutting-edge platform, powered by D&B Data Cloud's 520M+ Global Business Records with 2B+ annual updates for third-party risks, is an AI-powered solution that mitigates and monitors counterparty risk on a continual basis. D&B Risk Analytics uses best-in class risk data, including alerts for high-risk purchases and match points of more than a billion. This helps to drive informed decisions. Intelligent workflows allow for quick and thorough screening. Receive alerts on key business indicators.
Description
Achieve complete risk visibility at every stage of development, from design through coding to cloud deployment. Introducing the industry-leading Code Risk Platform™, which offers a comprehensive 360° overview of security and compliance threats across various domains, including applications, infrastructure, developers' expertise, and business ramifications. By making data-driven choices, you can enhance decision-making quality. Gain insight into your security and compliance vulnerabilities through a dynamic inventory that tracks application and infrastructure code behavior, developer knowledge, third-party security alerts, and their potential business consequences. Security professionals are often too busy to meticulously scrutinize every modification or to delve into every alert, but by leveraging their expertise efficiently, you can analyze the context surrounding developers, code, and cloud environments to pinpoint significant risky changes while automatically creating a prioritized action plan. Manual risk assessments and compliance evaluations can be a drag—they are often laborious, imprecise, and out of sync with the actual codebase. Since the design is embedded in the code, it’s essential to improve processes by initiating intelligent and automated workflows that reflect this reality. This approach not only streamlines operations but also enhances overall security posture.
Description
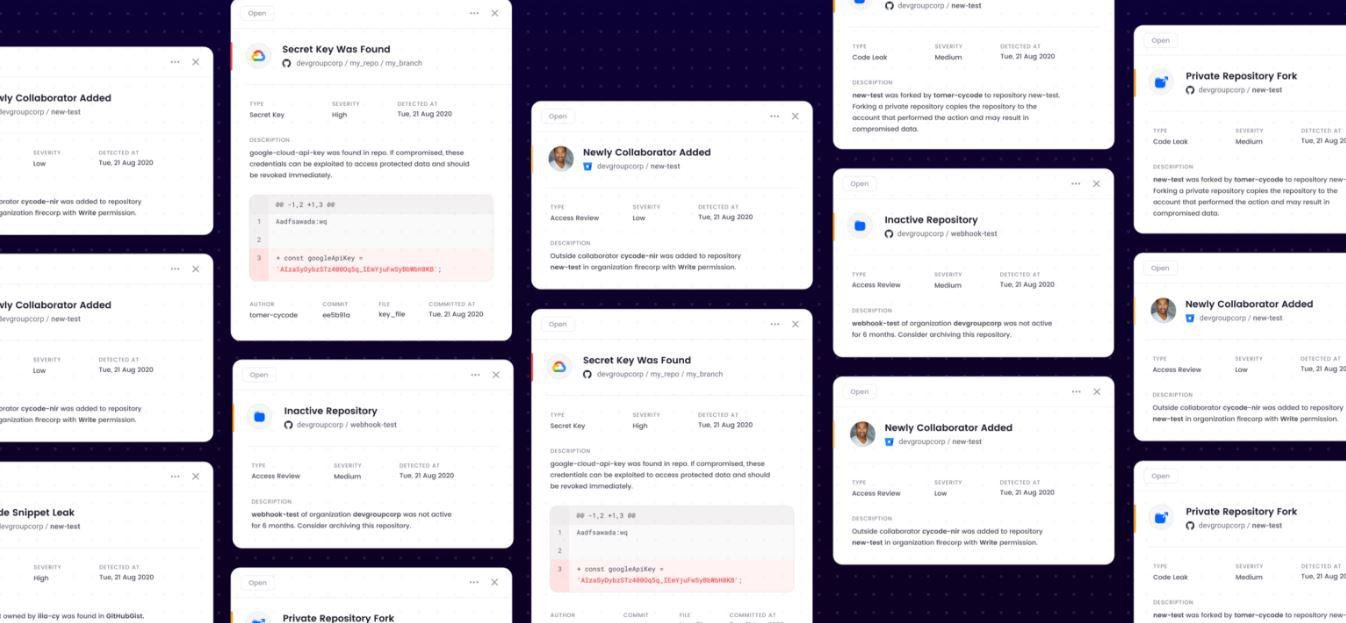
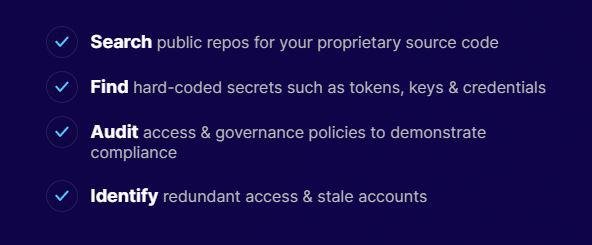
A comprehensive solution for ensuring security, governance, and pipeline integrity across all development tools and infrastructure is essential. Strengthen your source control management systems (SCM) by detecting secrets and leaks, while also safeguarding against code tampering. Examine your CI/CD configurations and Infrastructure-as-Code (IaC) for any security vulnerabilities or misconfigurations. Track any discrepancies between production systems’ IaC setups to thwart unauthorized code alterations. It's crucial to prevent developers from accidently making proprietary code public in repositories; this includes fingerprinting code assets and proactively identifying potential exposure on external sites. Maintain an inventory of assets, enforce stringent security policies, and easily showcase compliance throughout your DevOps ecosystem, whether it operates in the cloud or on-premises. Regularly scan IaC files for security flaws, ensuring alignment between specified IaC configurations and the actual infrastructure in use. Each commit or pull/merge request should be scrutinized for hard-coded secrets to prevent them from being merged into the master branch across all SCM platforms and various programming languages, thereby enhancing overall security measures. Implementing these strategies will create a robust security framework that supports both development agility and compliance.
API Access
Has API
Yes
API Access
Has API
No



Integrations
Amazon Web Services (AWS)
Yes
GitHub
Yes
GitLab
Yes
Jira
Yes
Kubernetes
Yes
Slack
Yes
Avalor
Yes
Axonius
No
CircleCI
No
Cobalt
No
Integrations
Amazon Web Services (AWS)
Yes
GitHub
Yes
GitLab
Yes
Jira
Yes
Kubernetes
Yes
Slack
Yes
Avalor
No
Axonius
Yes
CircleCI
Yes
Cobalt
Yes
Pricing Details
No price information available.
Free Trial
No
Free Version
No
Pricing Details
No price information available.
Free Trial
Yes
Free Version
No
Deployment
Web-Based
Yes
On-Premises
No
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Deployment
Web-Based
Yes
On-Premises
Yes
iPhone App
No
iPad App
No
Android App
No
Windows
No
Mac
No
Linux
No
Chromebook
No
Customer Support
Business Hours
Yes
Live Rep (24/7)
No
Online Support
Yes
Customer Support
Business Hours
No
Live Rep (24/7)
No
Online Support
Yes
Types of Training
Training Docs
No
Webinars
No
Live Training (Online)
Yes
In Person
No
Types of Training
Training Docs
Yes
Webinars
Yes
Live Training (Online)
Yes
In Person
No
Vendor Details
Company Name
Apiiro
Founded
2019
Country
United States
Website
apiiro.com
Vendor Details
Company Name
Cycode
Founded
2019
Country
Israel
Website
cycode.com
Product Features
Application Security
Analytics / Reporting
No
Open Source Component Monitoring
No
Source Code Analysis
No
Third-Party Tools Integration
No
Training Resources
No
Vulnerability Detection
No
Vulnerability Remediation
No
Cybersecurity
AI / Machine Learning
No
Behavioral Analytics
No
Endpoint Management
No
IOC Verification
No
Incident Management
No
Tokenization
No
Vulnerability Scanning
No
Whitelisting / Blacklisting
No
DevOps
Approval Workflow
No
Dashboard
No
KPIs
No
Policy Management
No
Portfolio Management
No
Prioritization
No
Release Management
No
Timeline Management
No
Troubleshooting Reports
No
